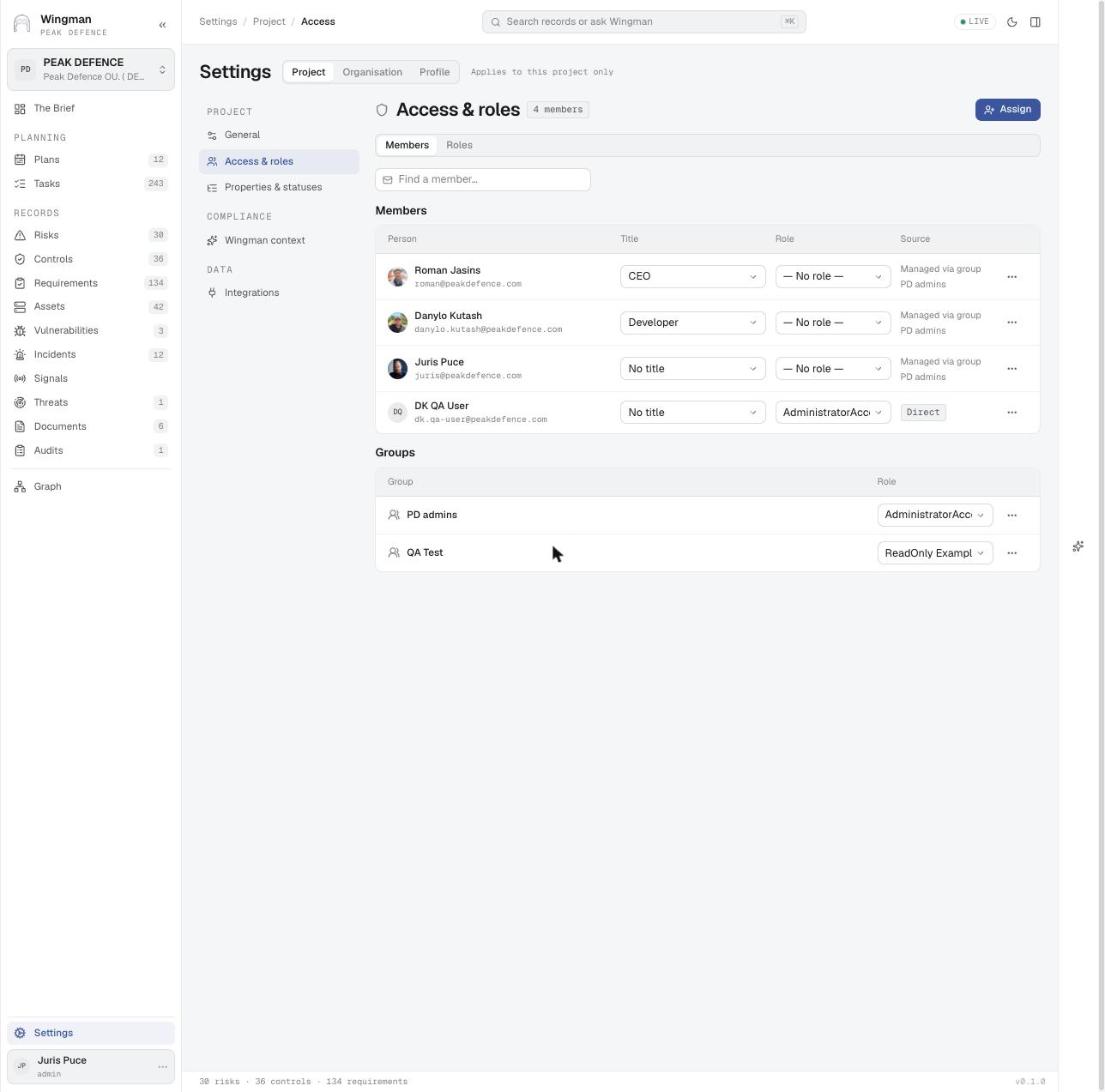
Roles and RACI
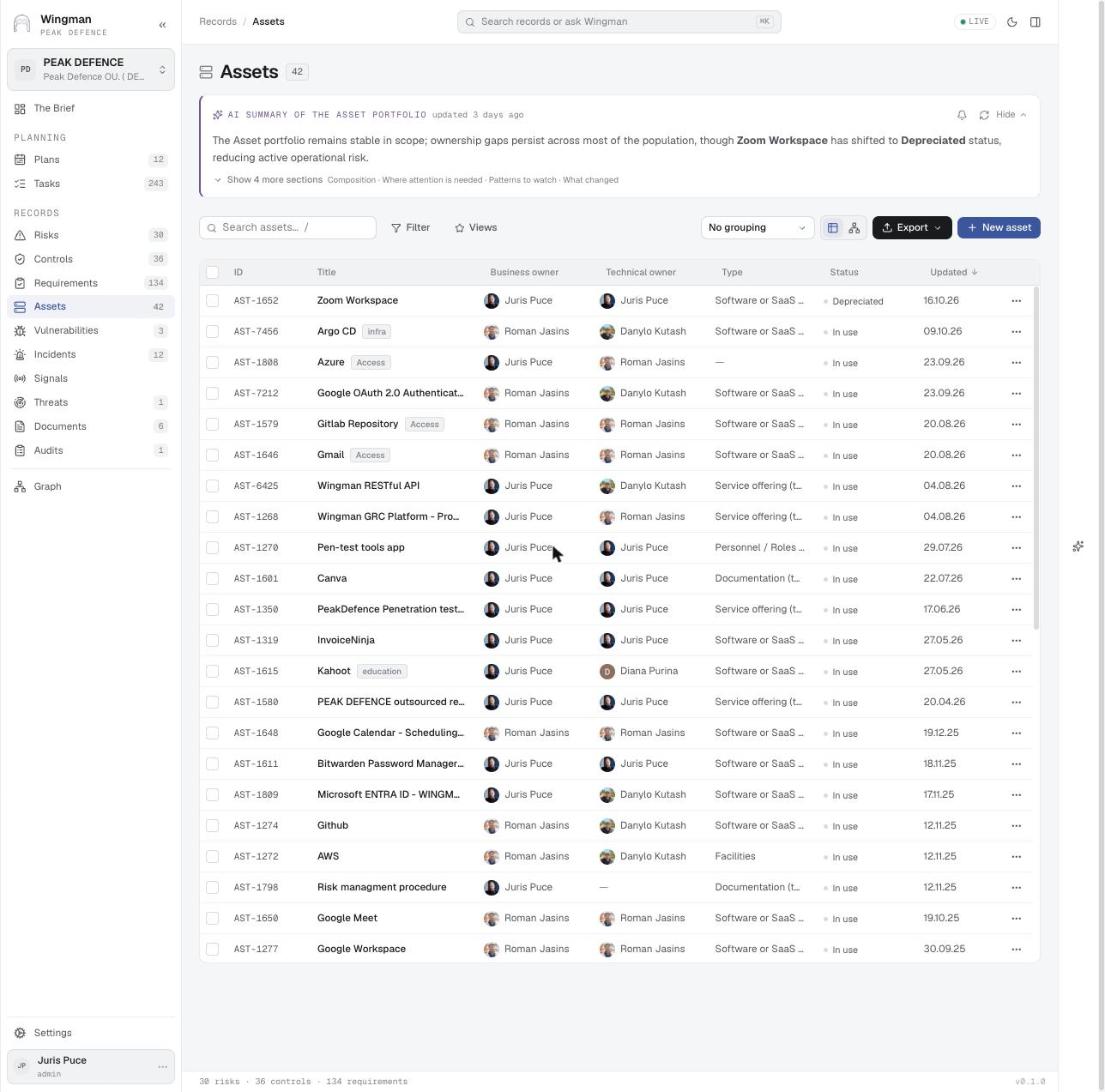
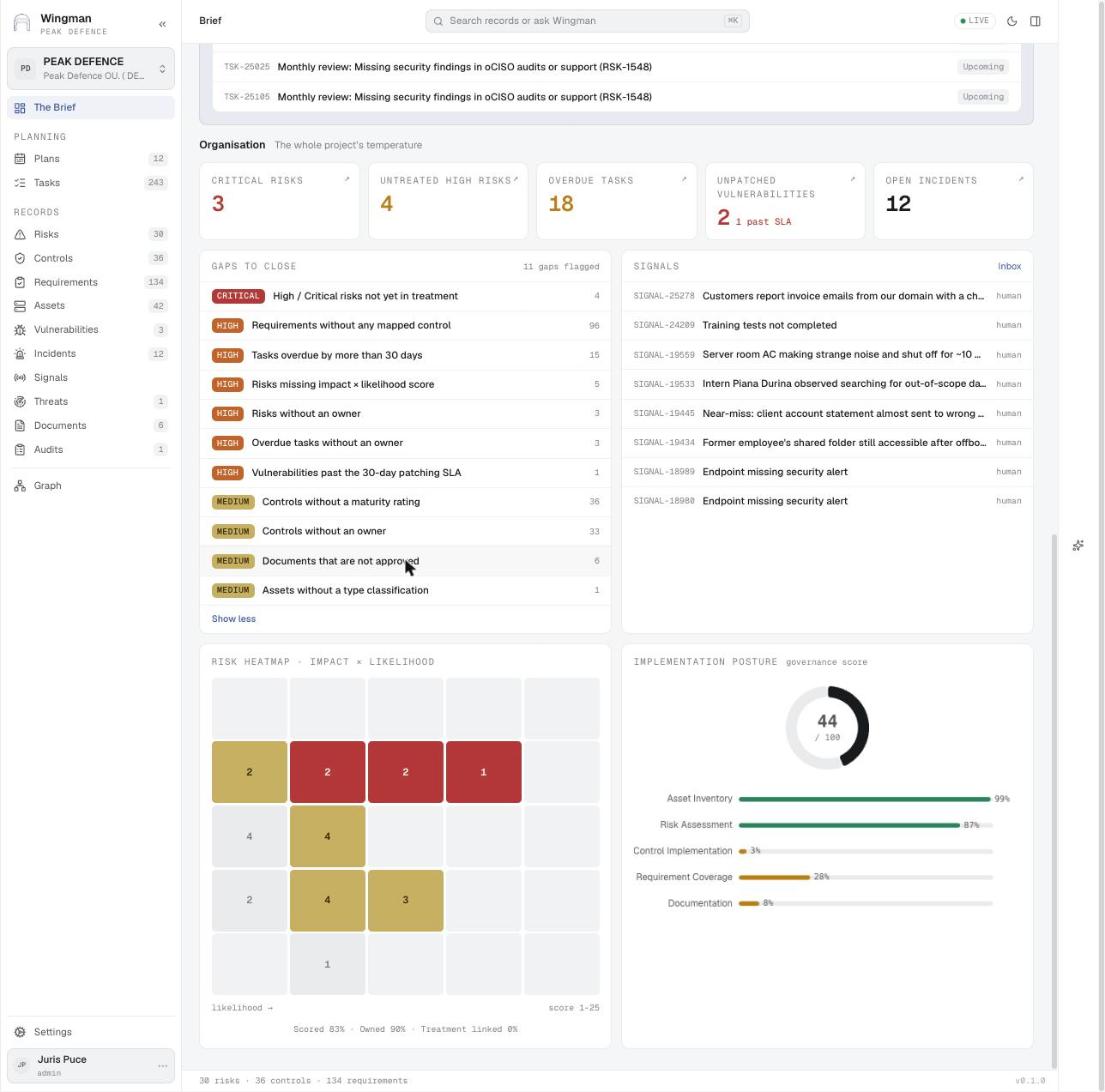
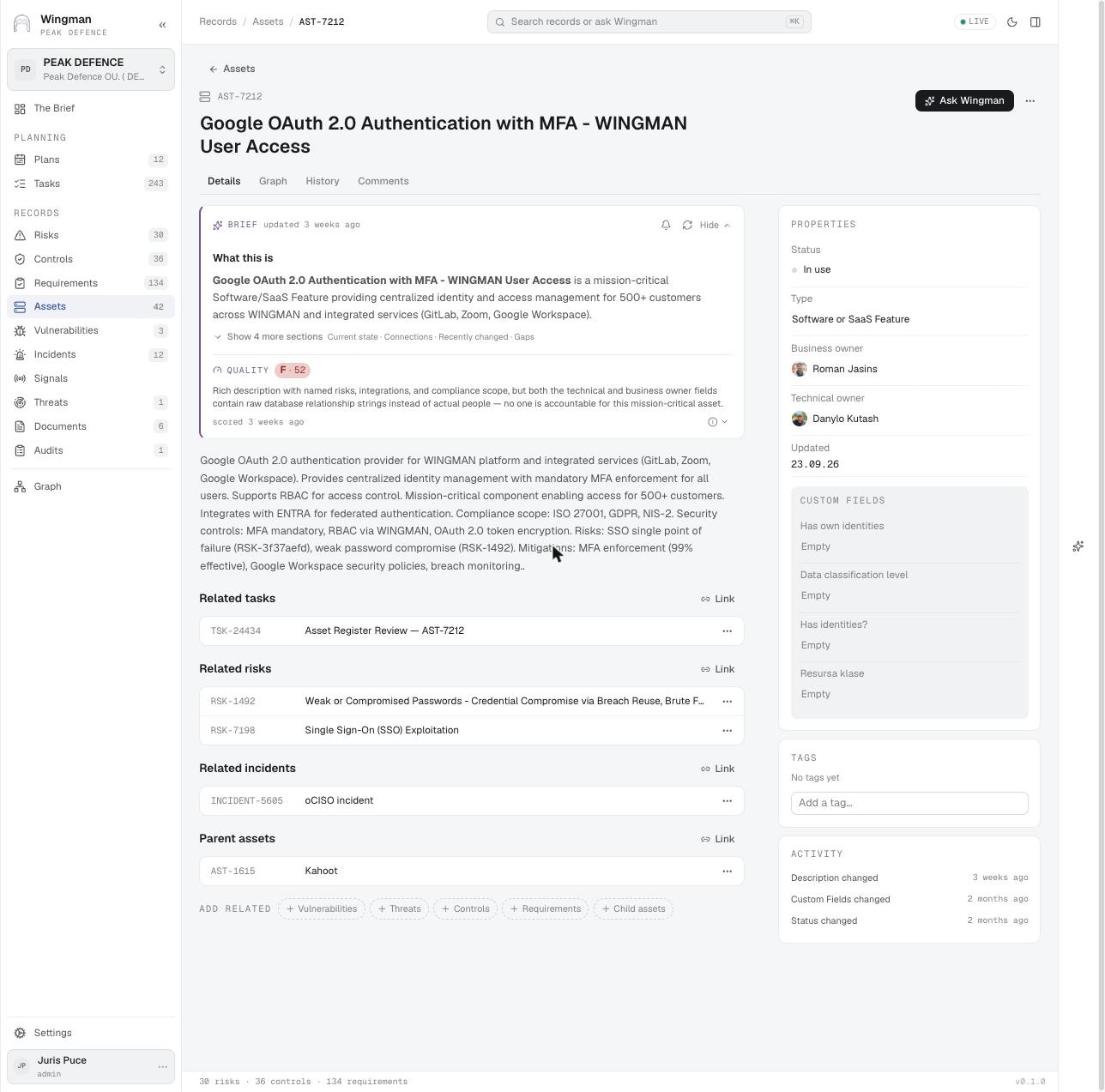
Make responsibilities explicit, and find gaps in coverage and conflicts in segregation of duties.
Typical requirementsISO 27001 5.3NIS2 Art. 20DORA Art. 5
Screens for this stage · Stage 1: Roles
Screens for this stage · Stage 2: RACI on every record
Screens for this stage · Stage 3: Coverage gaps
Sector angles
What this use case looks like under specific regulations.
NIS2
The cybersecurity manager, the management body and control owners are roles with written duties and deputies.
ISO 27001 / SOC 2
Control ownership is explicit and segregation of duties conflicts show up as gaps.
AI governance
Provider and deployer duties, human oversight and AI literacy sit with named roles.
GDPR
Controller, processor and DPO duties sit with roles, with the DPO's independence visible.
Videos

Plays from youtube-nocookie.com. YouTube sets no cookies until you press play.