ISO 27001 and SOC 2 Type 2
Keep the whole ISMS in one model, with control ownership, recurring reviews, management review and evidence that holds up over an audit period.
Typical requirementsISO/IEC 27001:2022ISO/IEC 27002:2022SOC 2 Trust Services CriteriaISO 27001 Annex A
Who it is forSoftware, SaaS and service companies certifying to ISO 27001 or reporting under SOC 2 Type 2, often both at once.
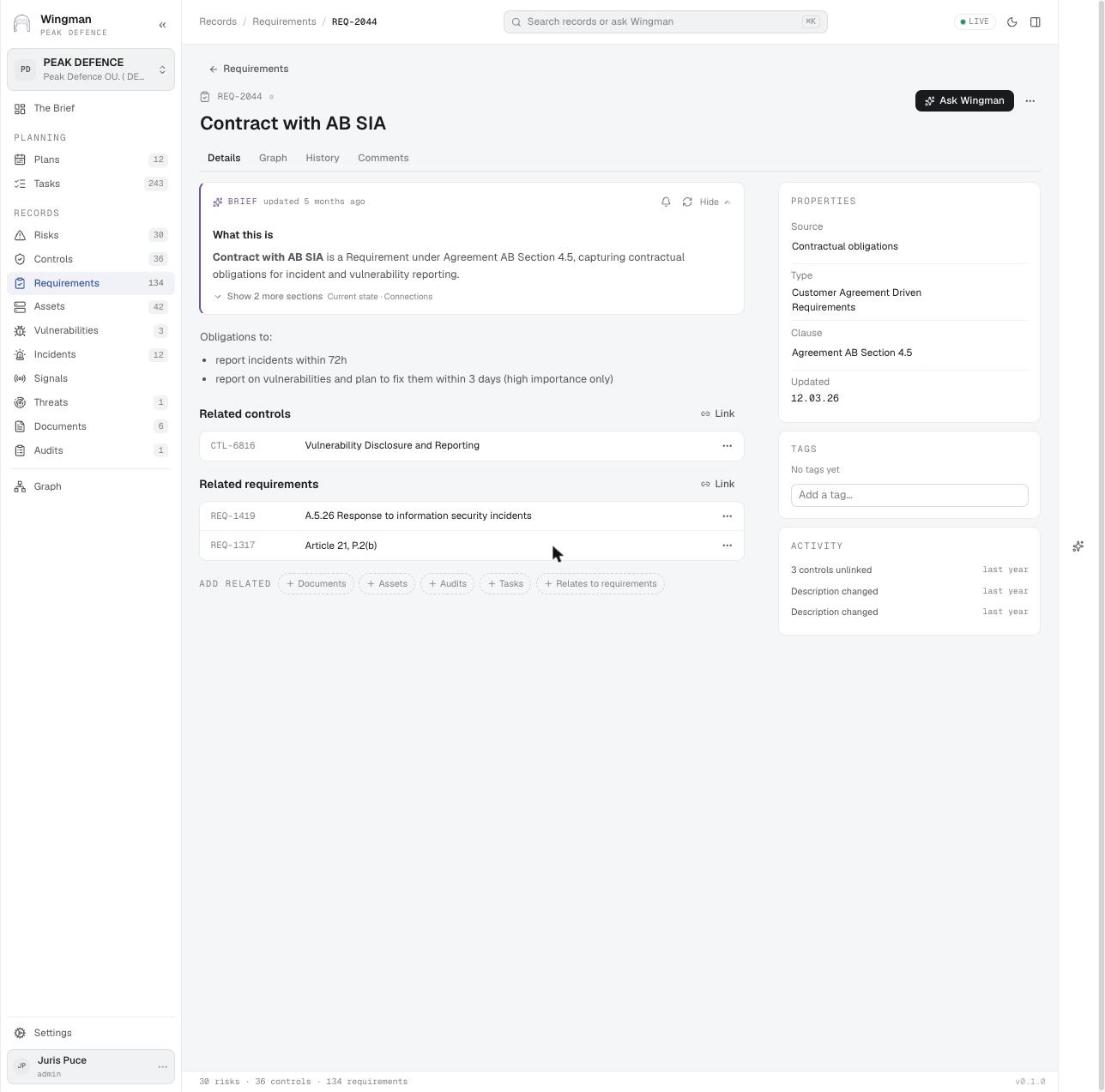
ISO 27001 and SOC 2 Type 2 ask for the same thing in different words: a defined scope, controls with owners, and proof that they operate. SOC 2 Type 2 adds a period: evidence must cover the whole observation window, not only the day of the audit.
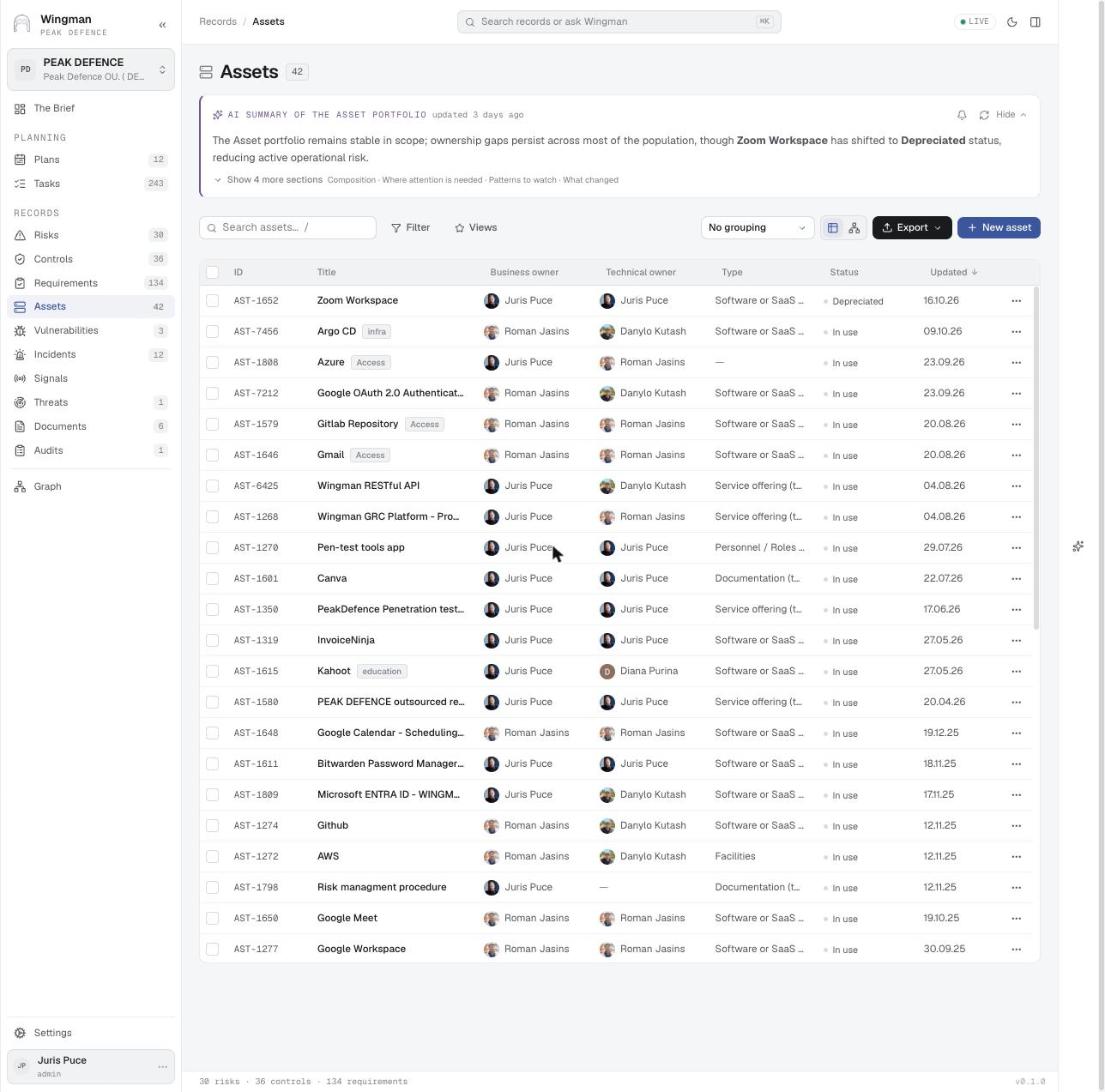
WINGMAN holds the whole ISMS as linked records: assets, risks, controls, documents, people, suppliers, evidence and the calendar of reviews. Because Annex A and the Trust Services Criteria map to the same controls, one set of evidence serves both. The Statement of Applicability is not a document someone updates once a year: it is generated in real time from the controls actually in operation, their linked risks and their evidence.
Videos


Plays from youtube-nocookie.com. YouTube sets no cookies until you press play.
Registers WINGMAN keeps
Each register is a set of linked records in one model, not a separate spreadsheet. Pick an entity to see it in the data model.
Asset inventory
Information and associated assets with owners and classification, reviewed on a schedule (A.5.9).
Risk register and treatment plan
Risks with owners, ratings and treatments, linked to the controls in the Statement of Applicability.
Live Statement of Applicability
Generated from the control register, not kept as a separate spreadsheet. Applicability, justification, linked risks, status and evidence per Annex A control, with approved versions kept for the auditor.
Control register
Annex A and Trust Services Criteria controls with owners, frequency, status and evidence.
People and access
Staff and contractors with roles, training, policy acknowledgements and the access they hold, for joiner, mover and leaver checks and access reviews.
Supplier register
Suppliers and subservice organisations with the services they provide, assessments and contracts.
Evidence library
Proof per control and period, approved by the owner, with expiry, ready for sampling.
Compliance calendar
Reviews, internal audits, management reviews, tests and trainings as one yearly plan.
The governance cycle on the model
Step through how the regulation runs on WINGMAN records, from scope to proof.
Screens for this stage · Stage 1: Scope and context
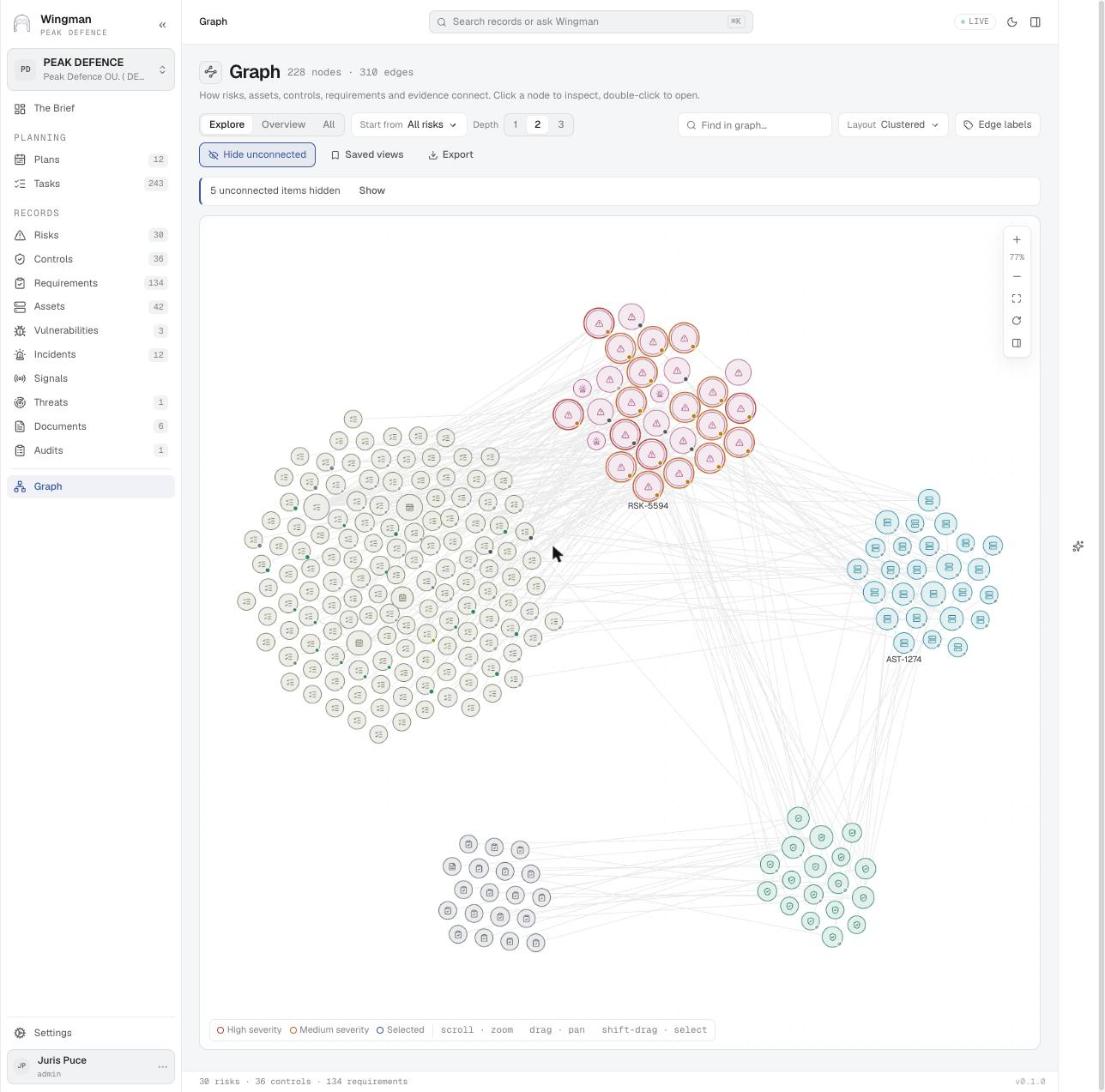
Screens for this stage · Stage 2: One control set, two frameworks
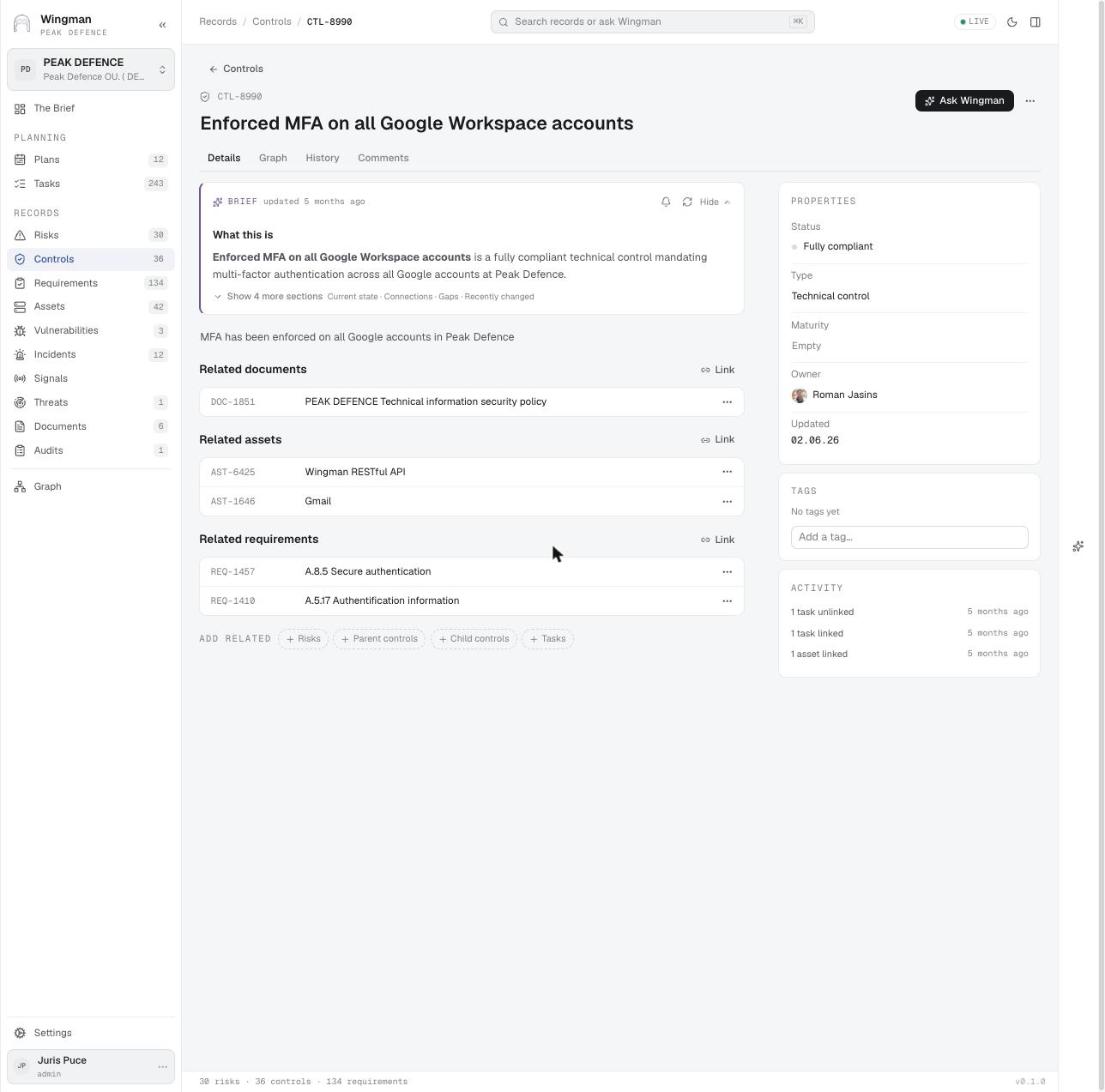
Screens for this stage · Stage 4: Control ownership
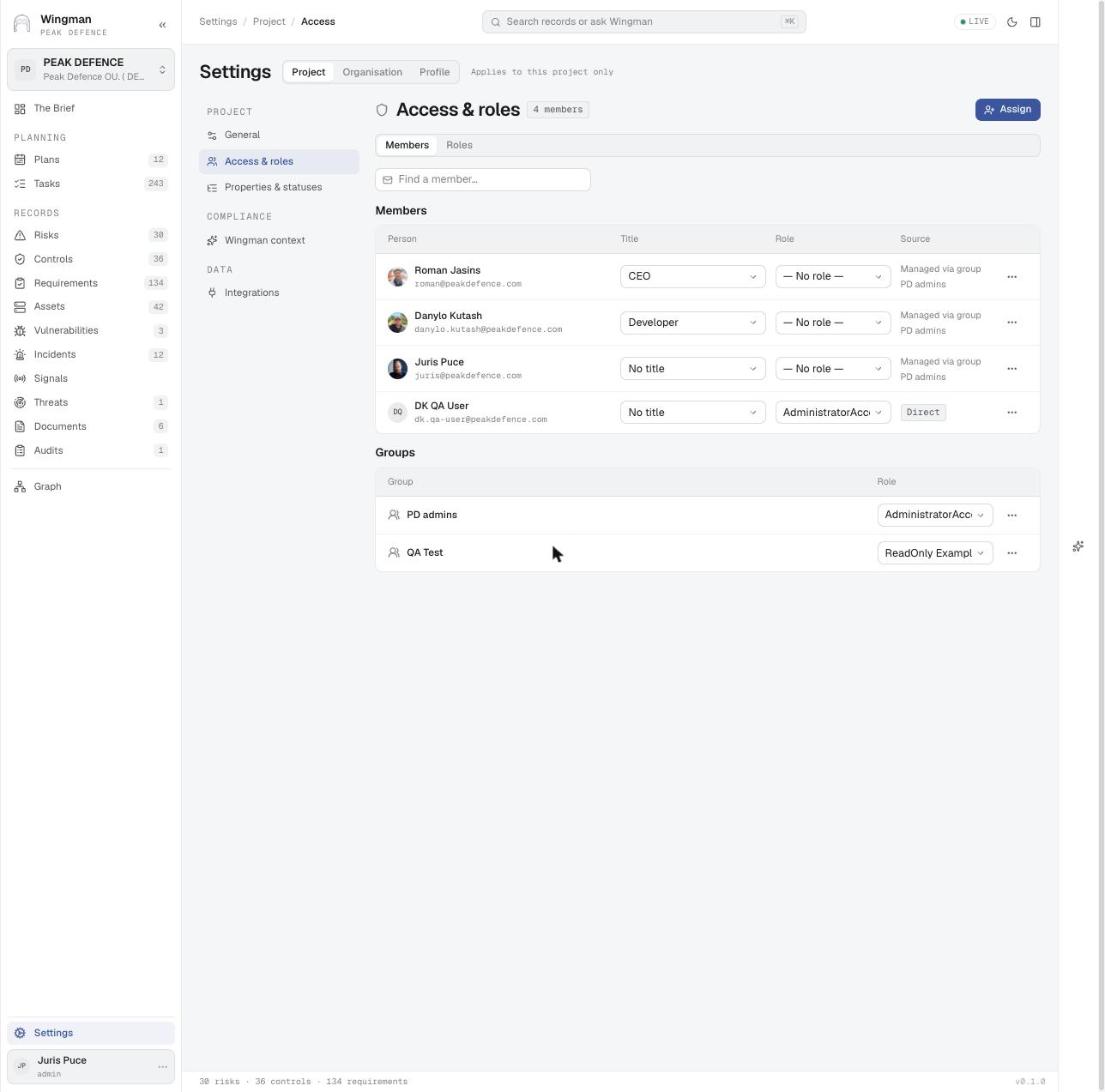
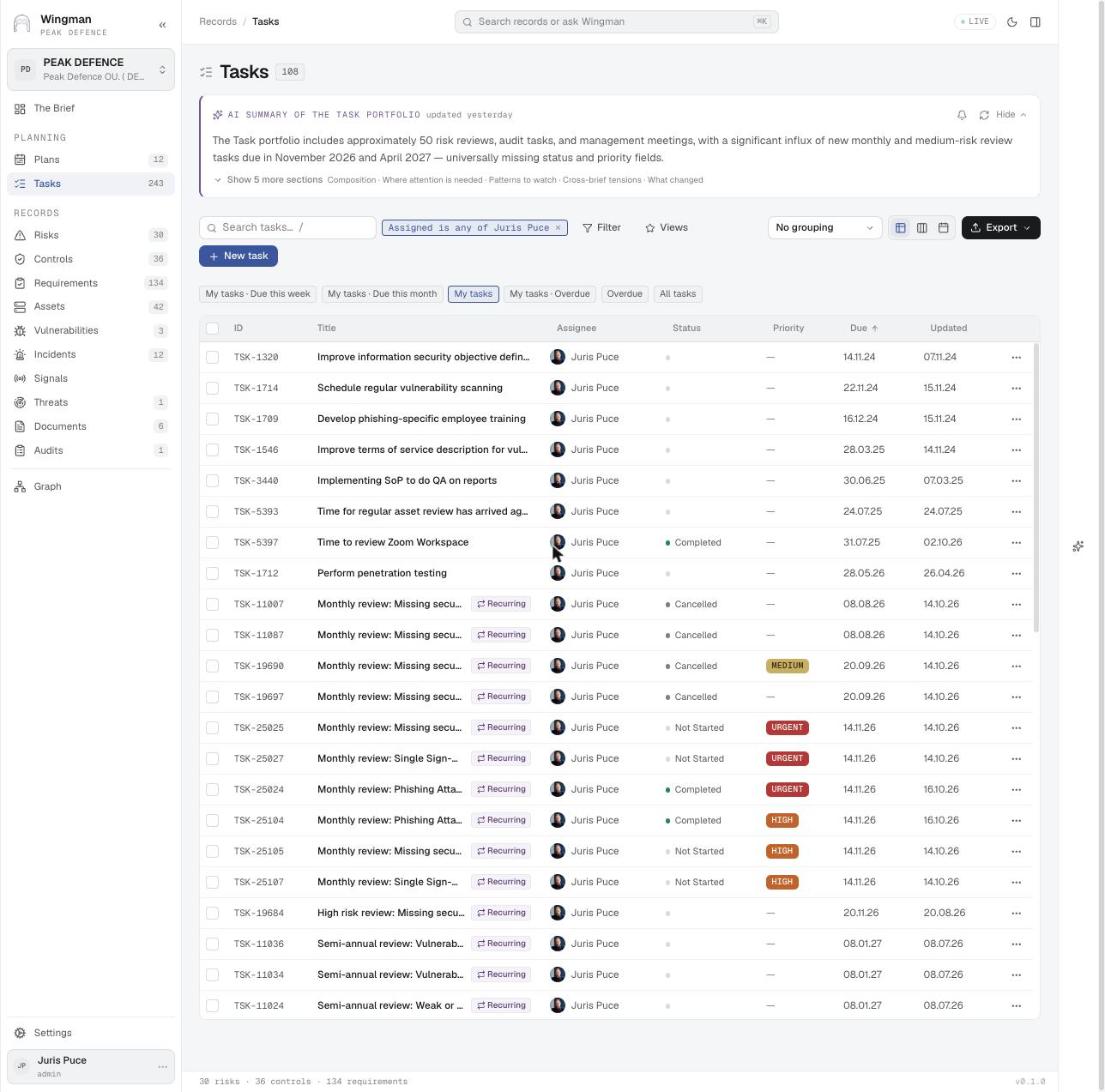
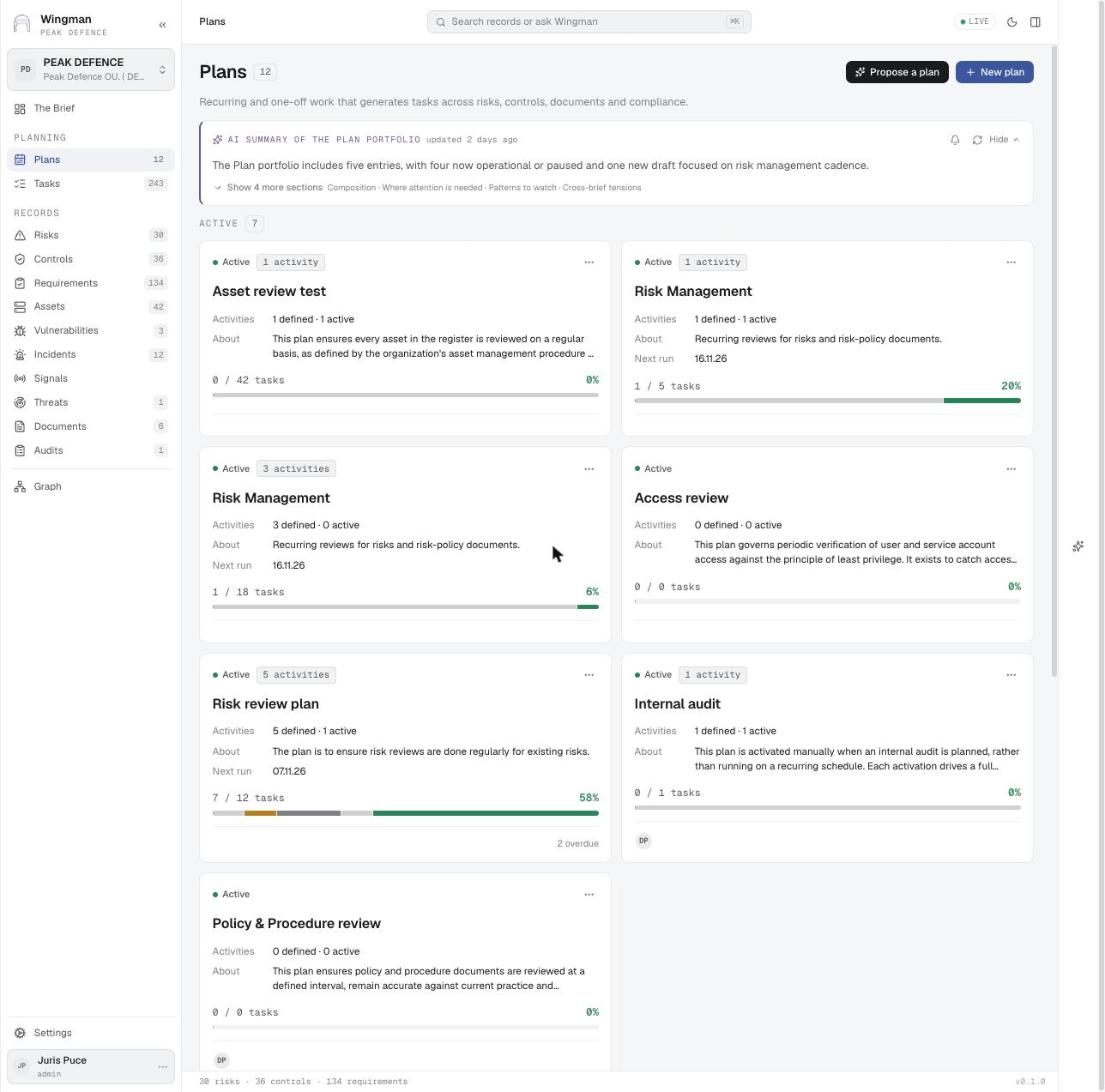
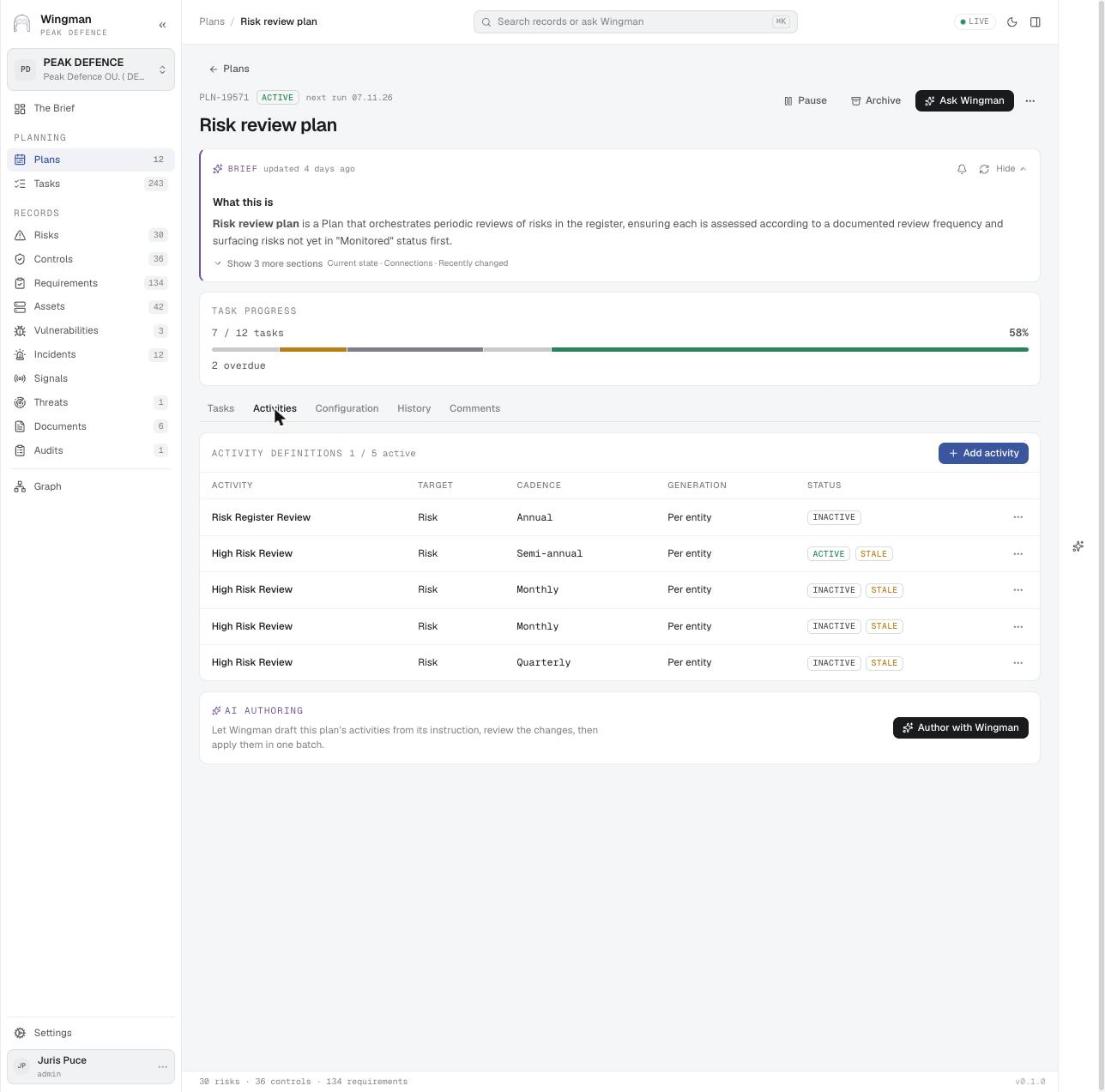
Screens for this stage · Stage 5: Recurring reviews
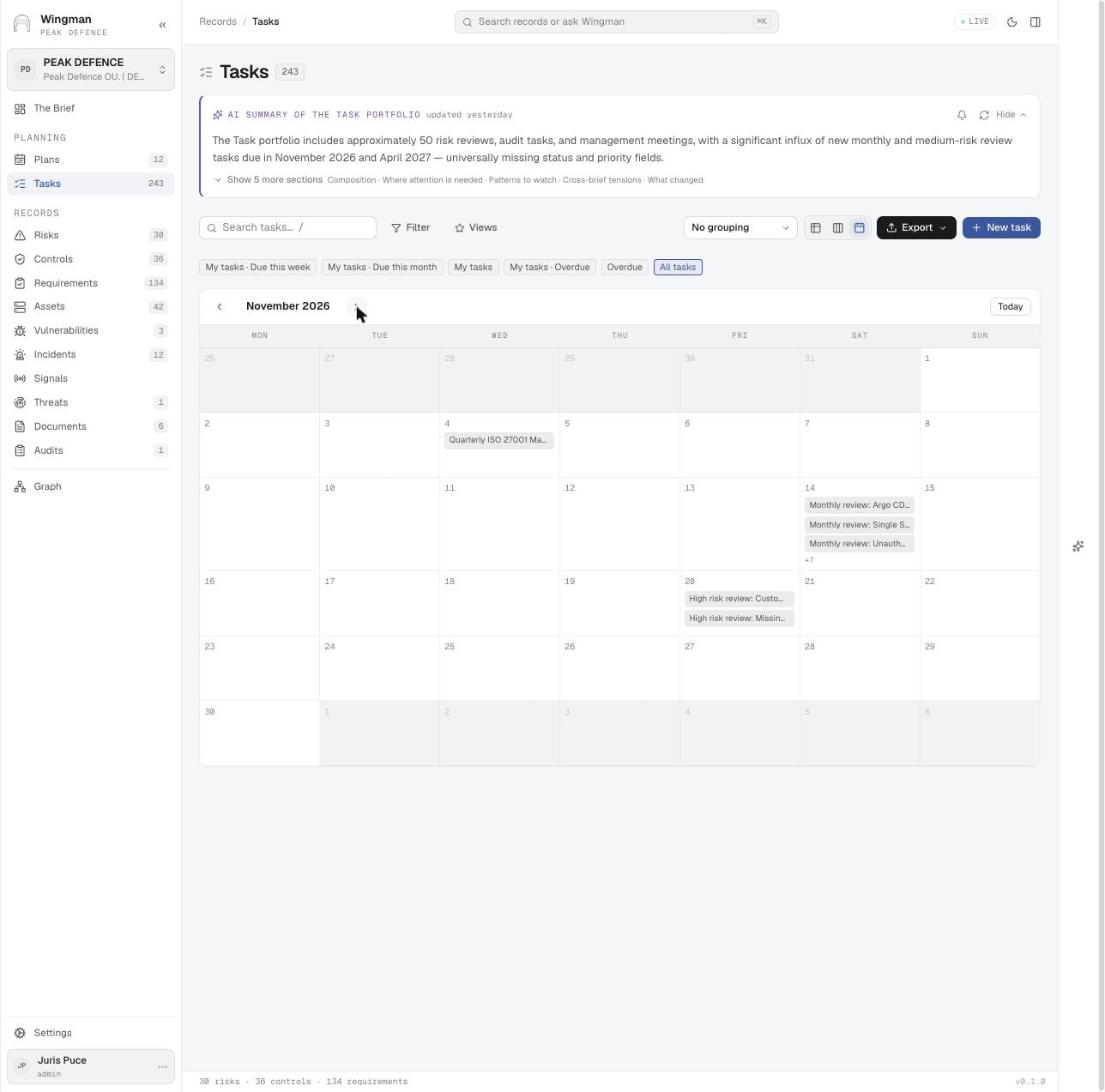
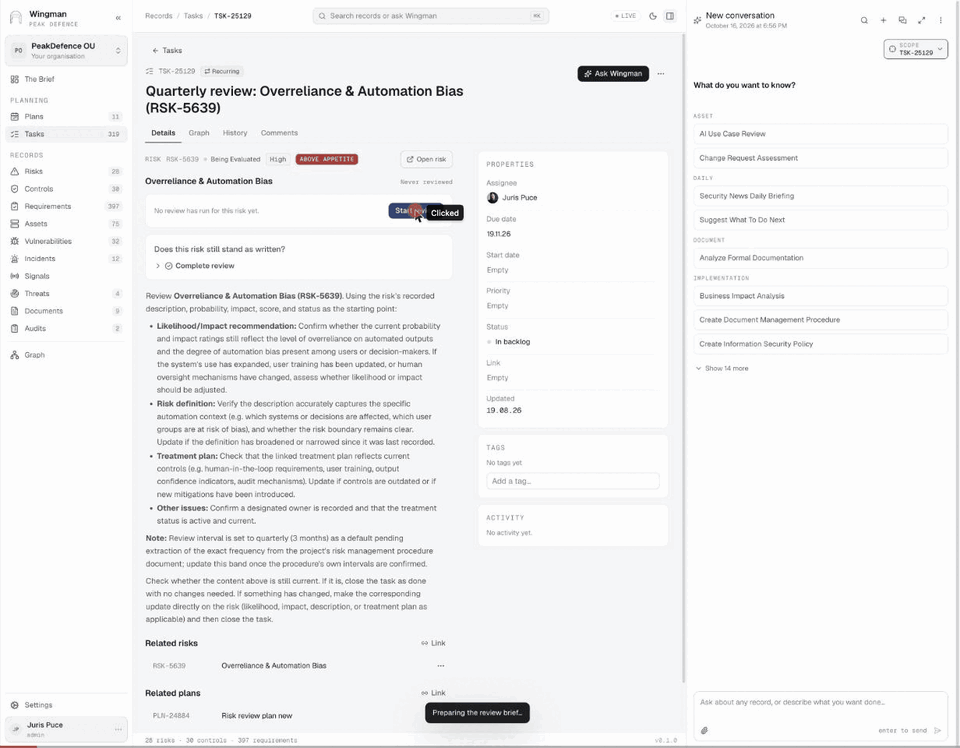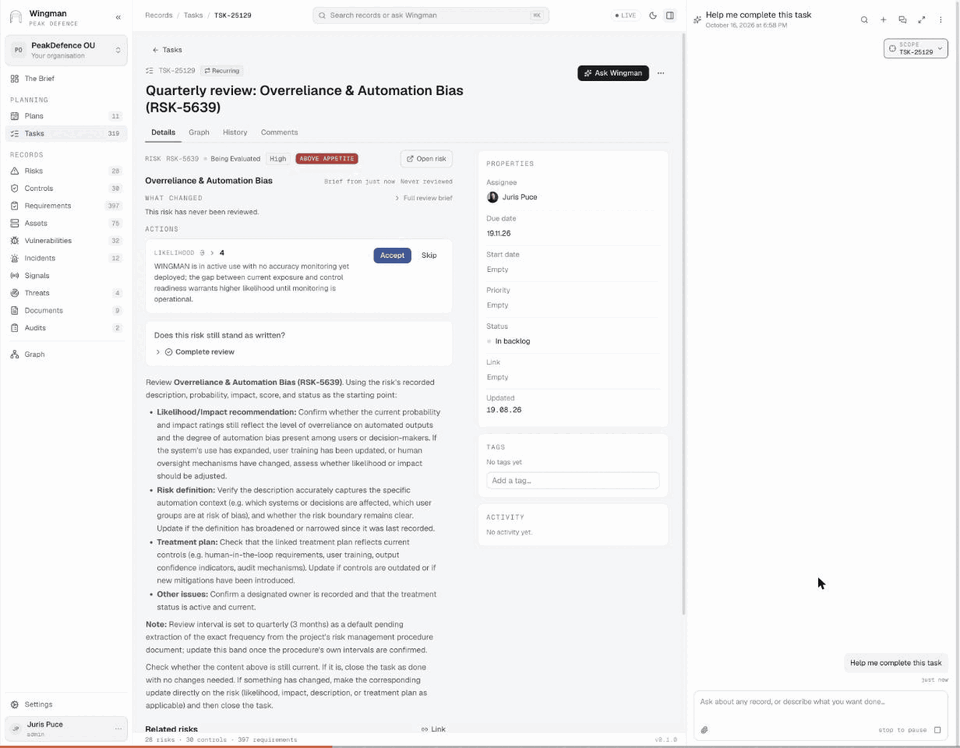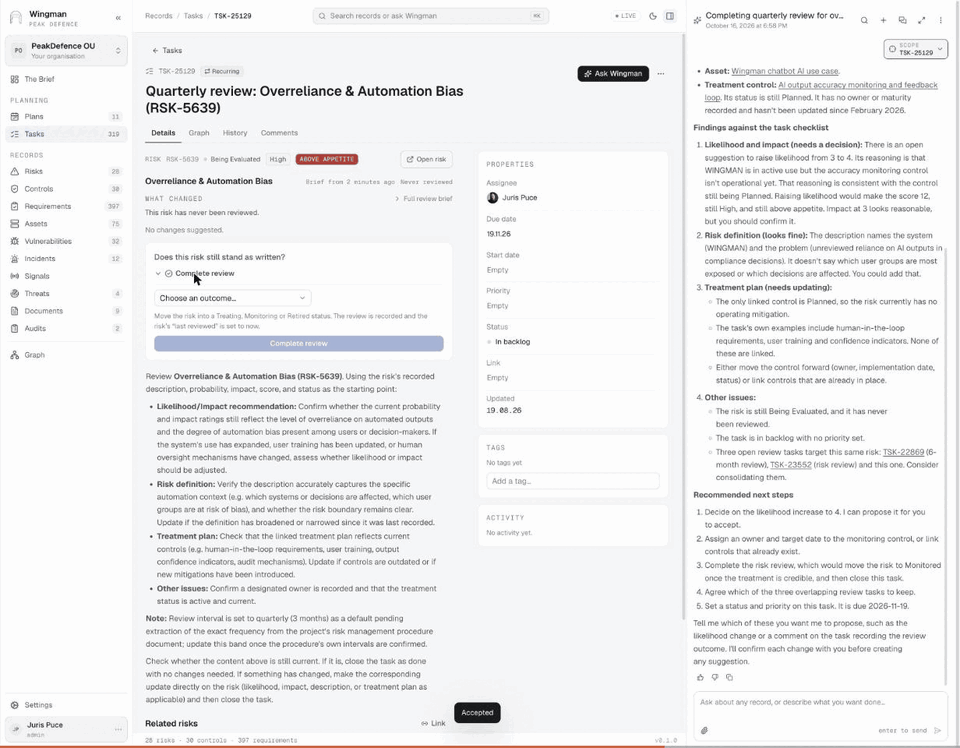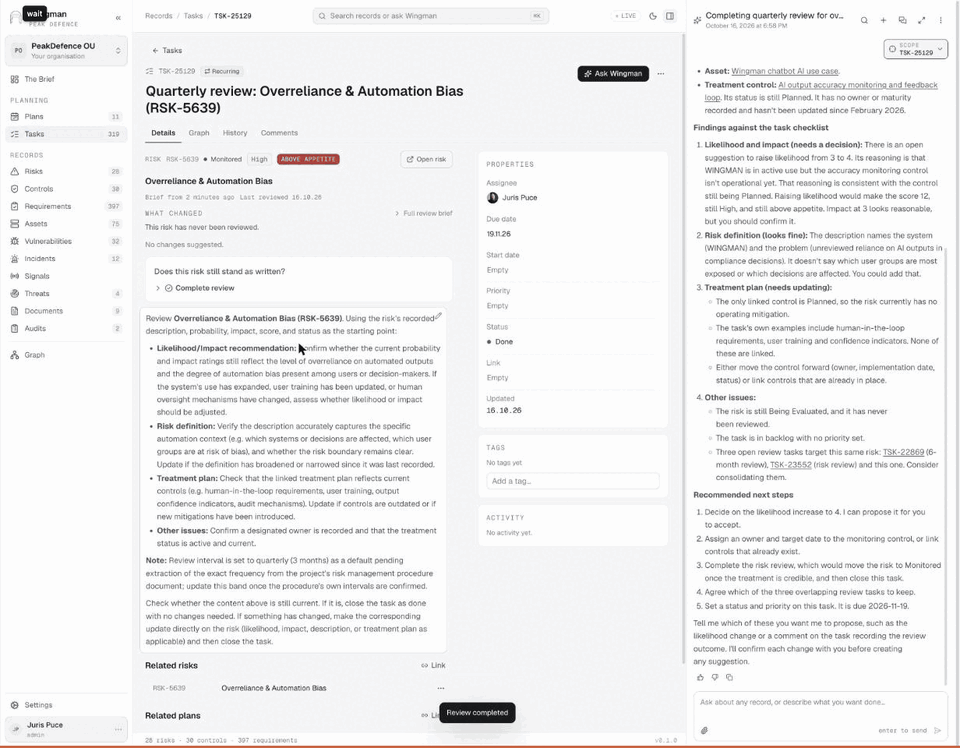 GIF
Screens for this stage · Stage 7: Internal audit and management review
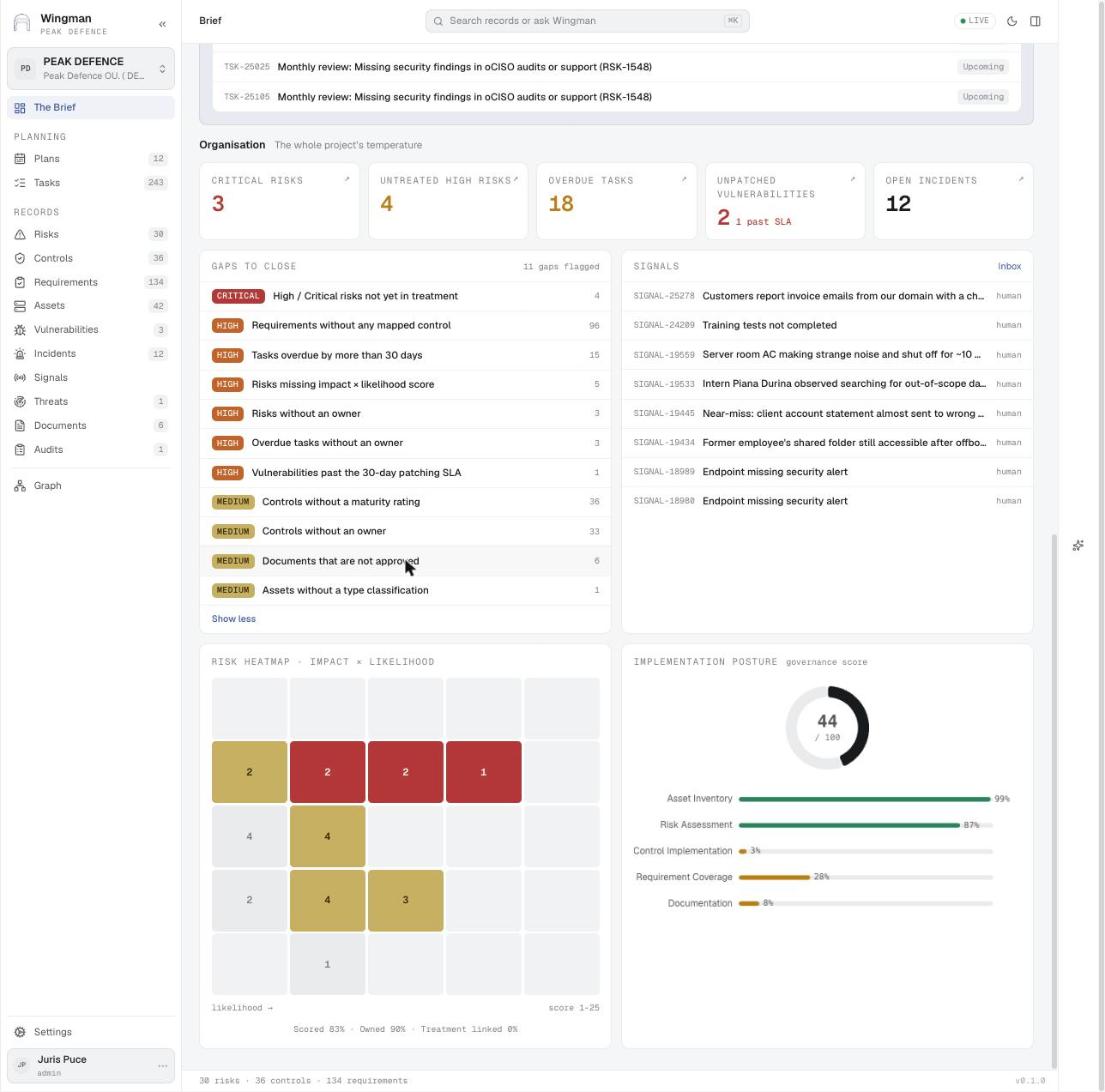
Use cases from this angle
The same use cases, with what changes for this regulation.
Operations
Regular reviews
Asset, risk, document and access reviews run on schedule, each leaving a task and evidence behind.
Accountability
Roles and RACI
Control ownership is explicit and segregation of duties conflicts show up as gaps.
Assurance
Auditing
Internal audits per clause with findings, conclusions and corrective actions, ready for the certification body or the SOC 2 auditor.
Assurance
Audit with several scopes
One audit programme covering several products, or ISO 27001 and SOC 2 at once, without duplicate evidence.
Compliance
Management review
Inputs required by clause 9.3 come from live records; decisions become tracked tasks.
Risk
Risk review and treatment
Risk assessment and treatment on a set cycle. A treatment decision changes the live Statement of Applicability straight away.
Operations
Change management
Changes are assessed for security impact, and the change record is evidence for change management controls.
Operations
Security operations control
Operational controls such as backups, logging and patching produce evidence every time they run.
Questions it answers
Did every control operate for the whole audit period?
From each control to its evidence by period, showing gaps and expired items before sampling begins.
What does our Statement of Applicability say today?
It is generated from the controls in operation at this moment, so status and justification match reality. Controls claimed as implemented without valid evidence are flagged before the auditor sees them.
Which reviews are overdue?
From the compliance calendar to each review task, its owner and due date.
Who owns this control now that its owner has left?
Ownership sits on the role. Assign the role to a successor and the control, its tasks and its evidence follow.
Are we ready for the management review?
Audit results, risk changes, incidents, objectives and open actions are pulled from records, not collected by email.
Other sectors and regulations
NIS2 and national cybersecurity law
Run the information security office of an essential or important entity from one registry of suppliers, assets, risks, incidents, vulnerabilities, threats and tasks.
Financial sector – DORA, MiCA and supervisory expectations
Run operational, financial, reputational and other non-financial risk management on one model, and catch the events that should move it.
AI governance – ISO 42001, EN 18286 and the EU AI Act
Treat each AI use case as an asset with its own risks, controls and work plan, and show conformity with the EU AI Act from the same records.
Cyber Resilience Act
Design CRA compliance into how products are built and supported, from risk assessment and SBOM to vulnerability handling and reporting.
GDPR and data protection
Keep the record of processing, DPIAs, processors, data subject requests and breaches as linked records, so accountability can be shown at any time.