Security operations control
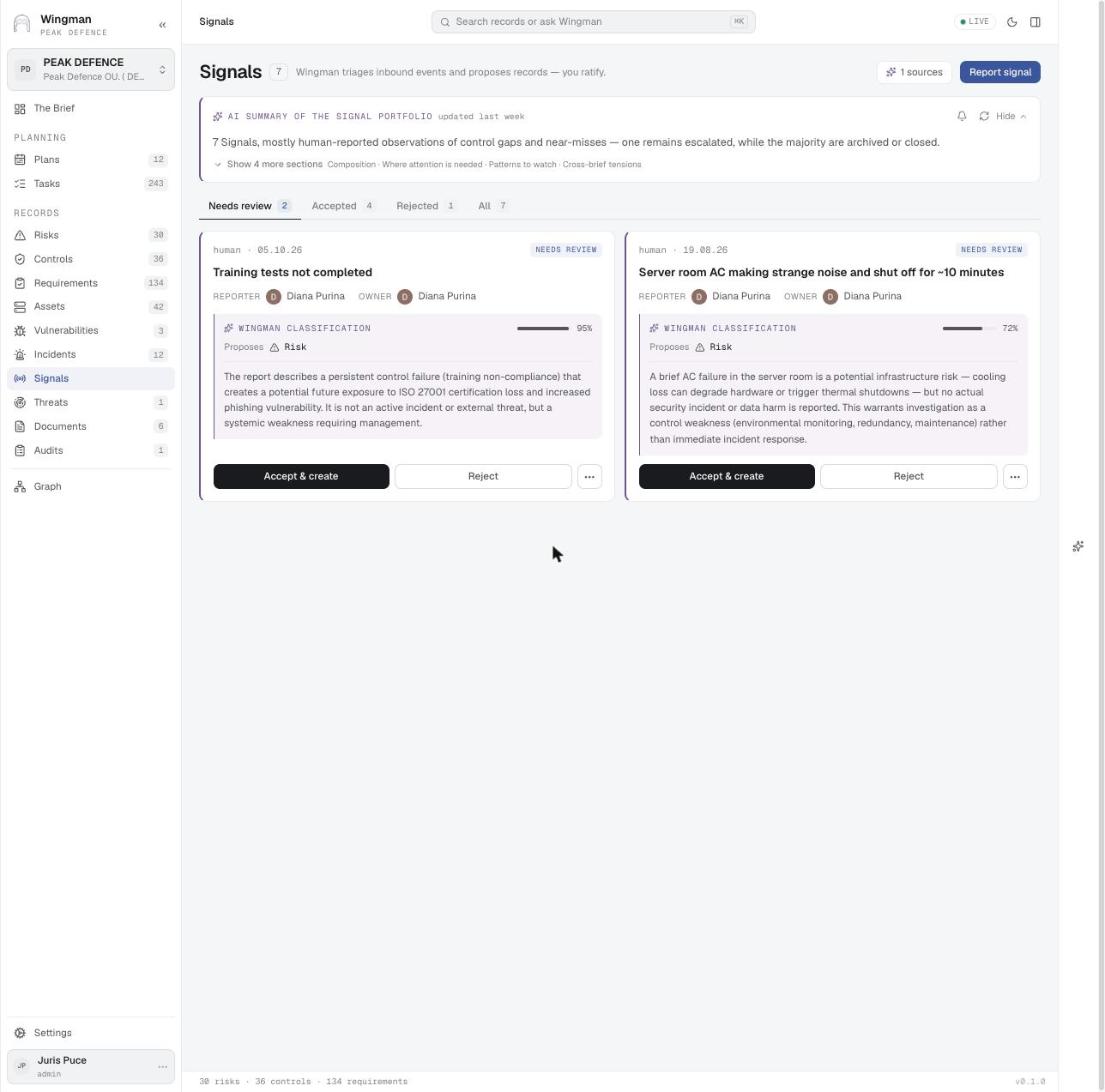
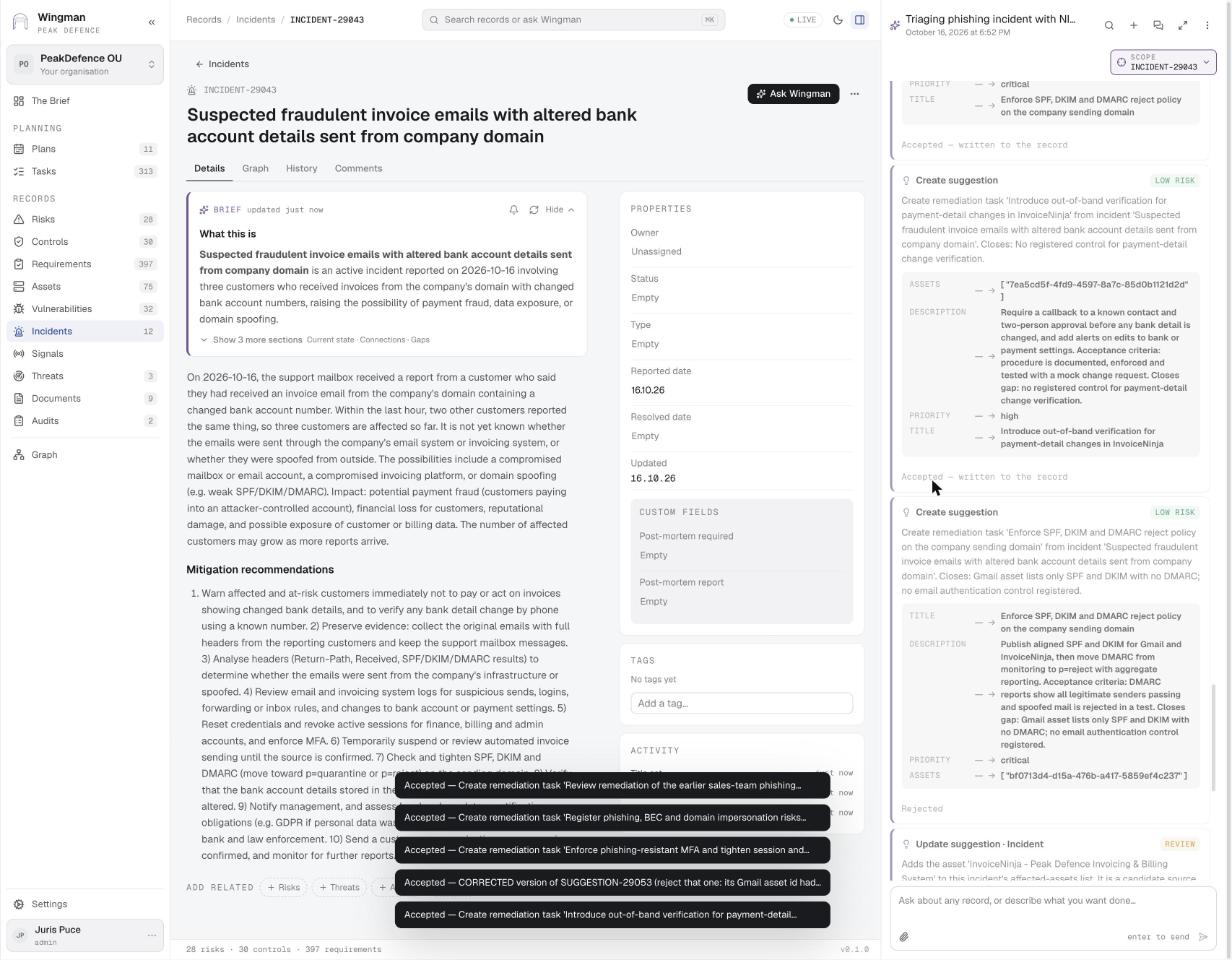
Run security work through plans and tasks, with briefs, reminders and escalations, and ask "what needs to be done" against everything the model knows.
Typical requirementsISO 27001NIS2 Art. 21
Screens for this stage · Stage 1: Plans
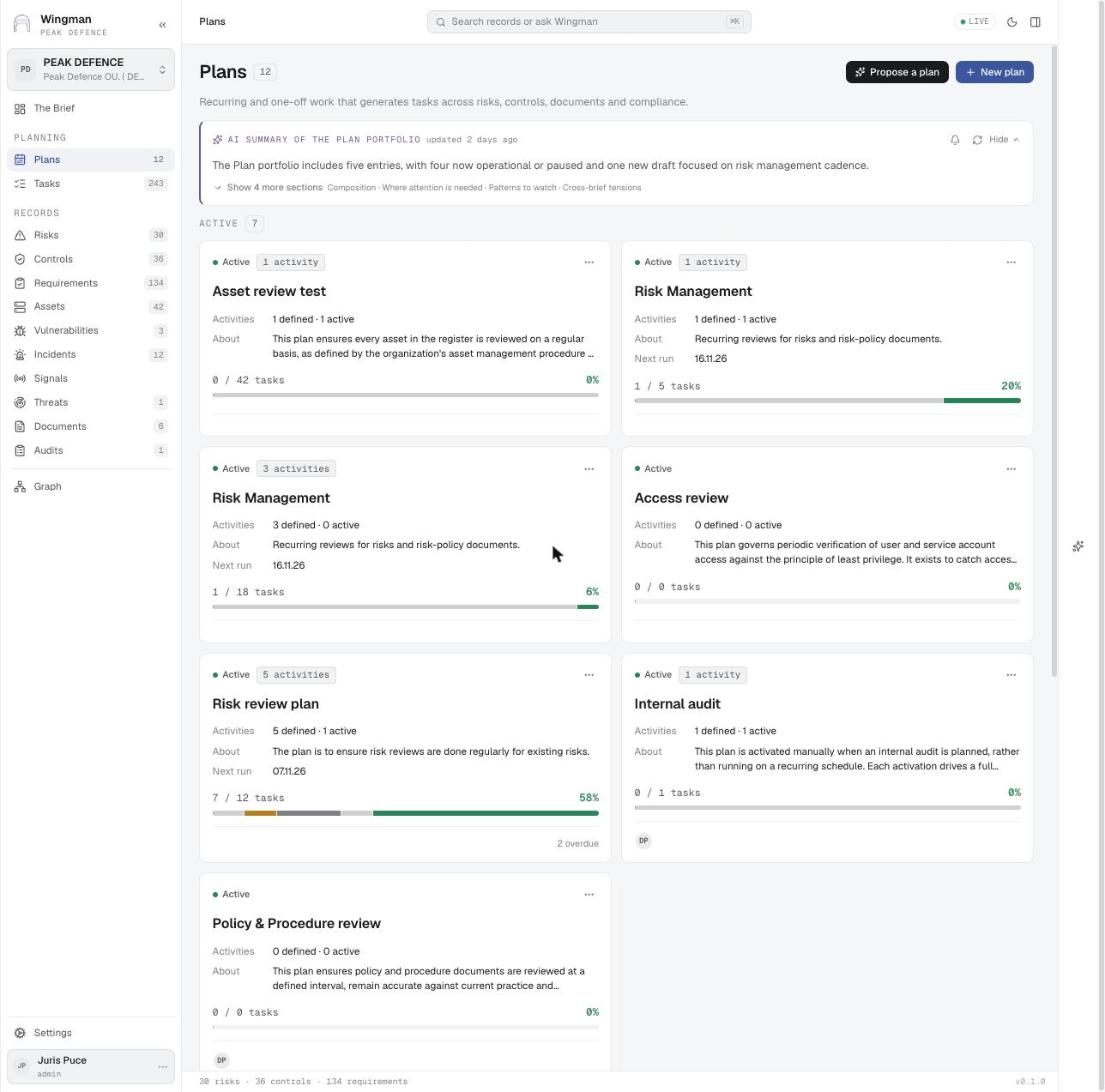
Screens for this stage · Stage 2: Daily work
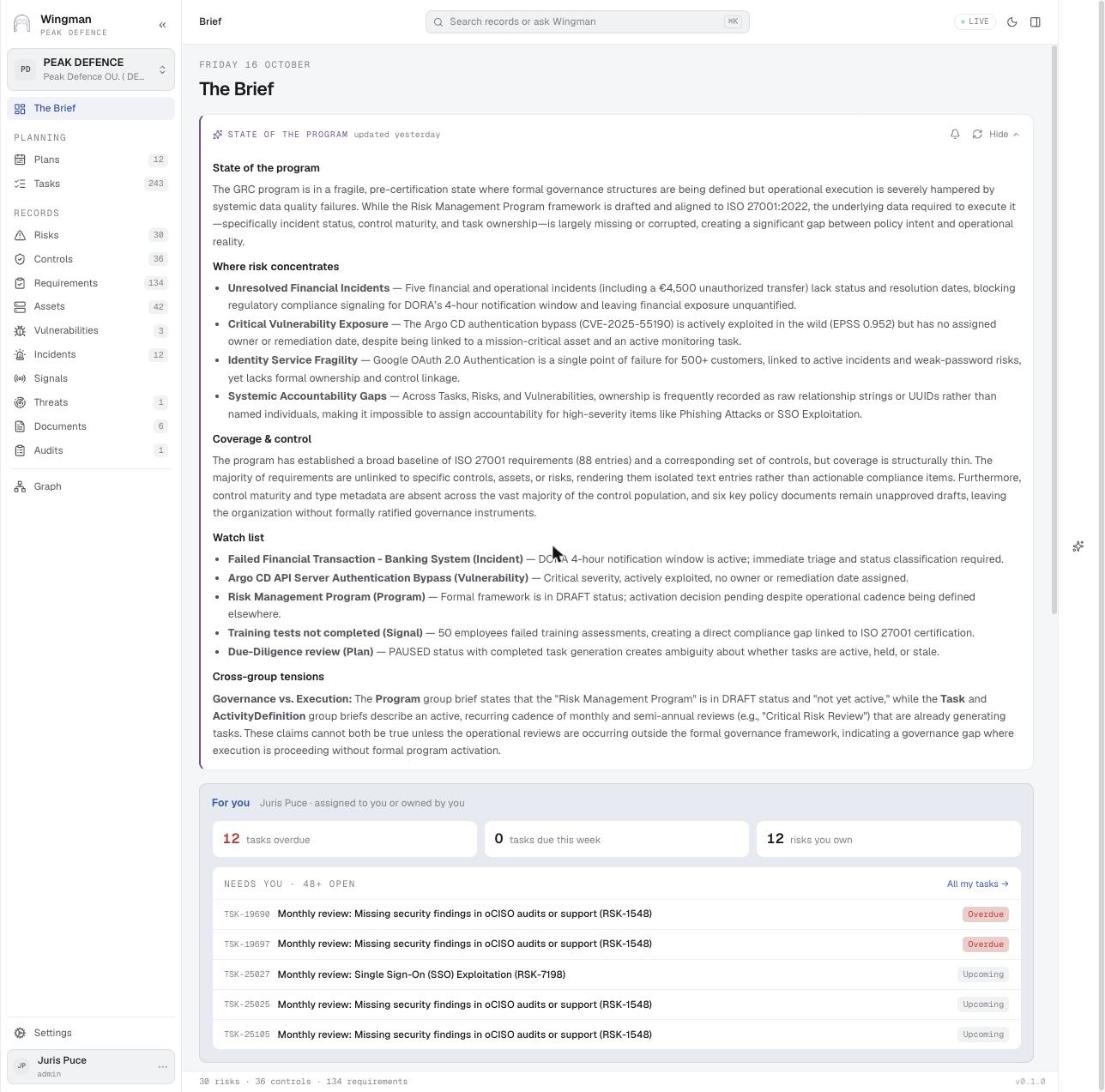
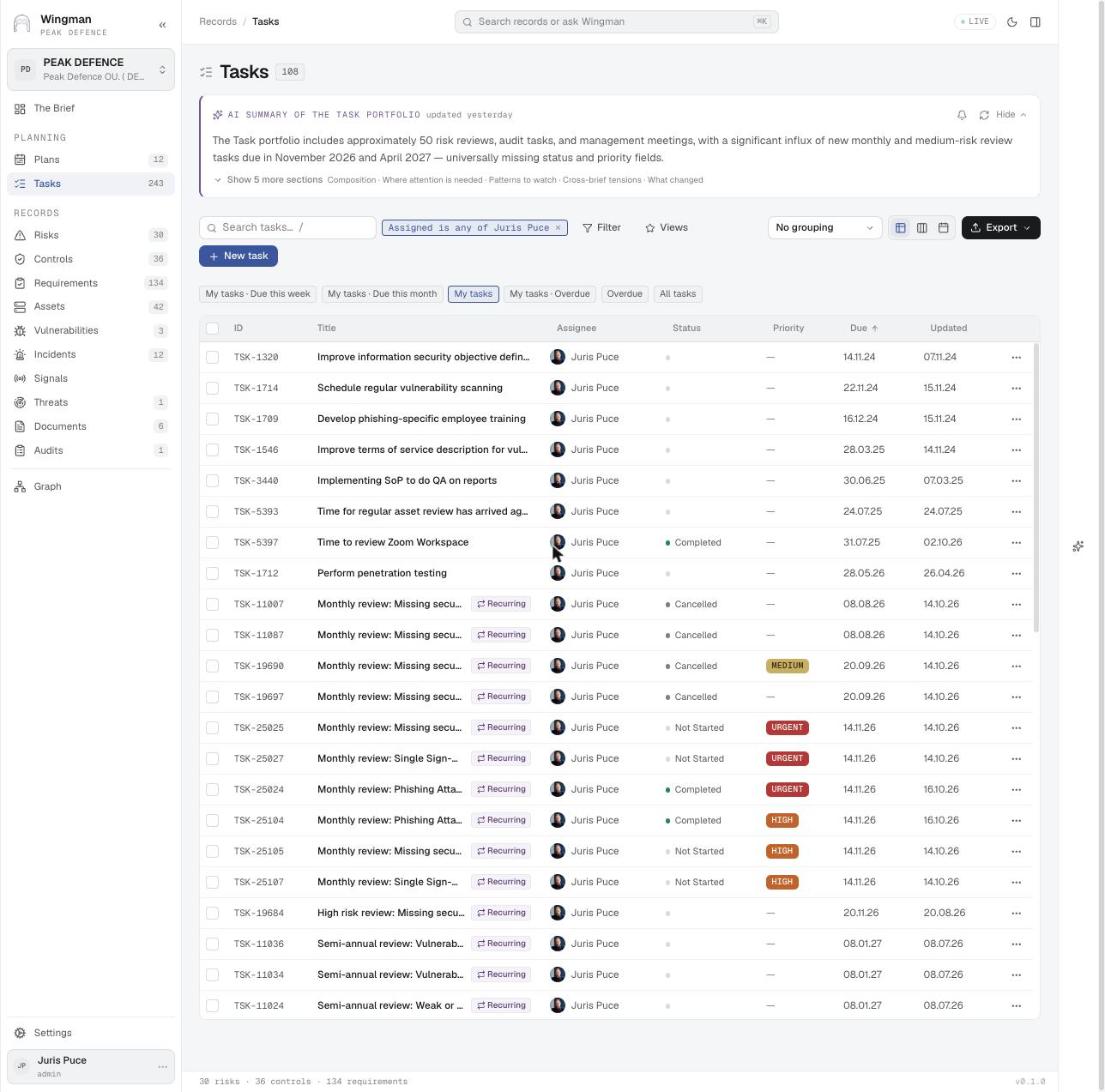
Screens for this stage · Stage 3: Briefs and reminders
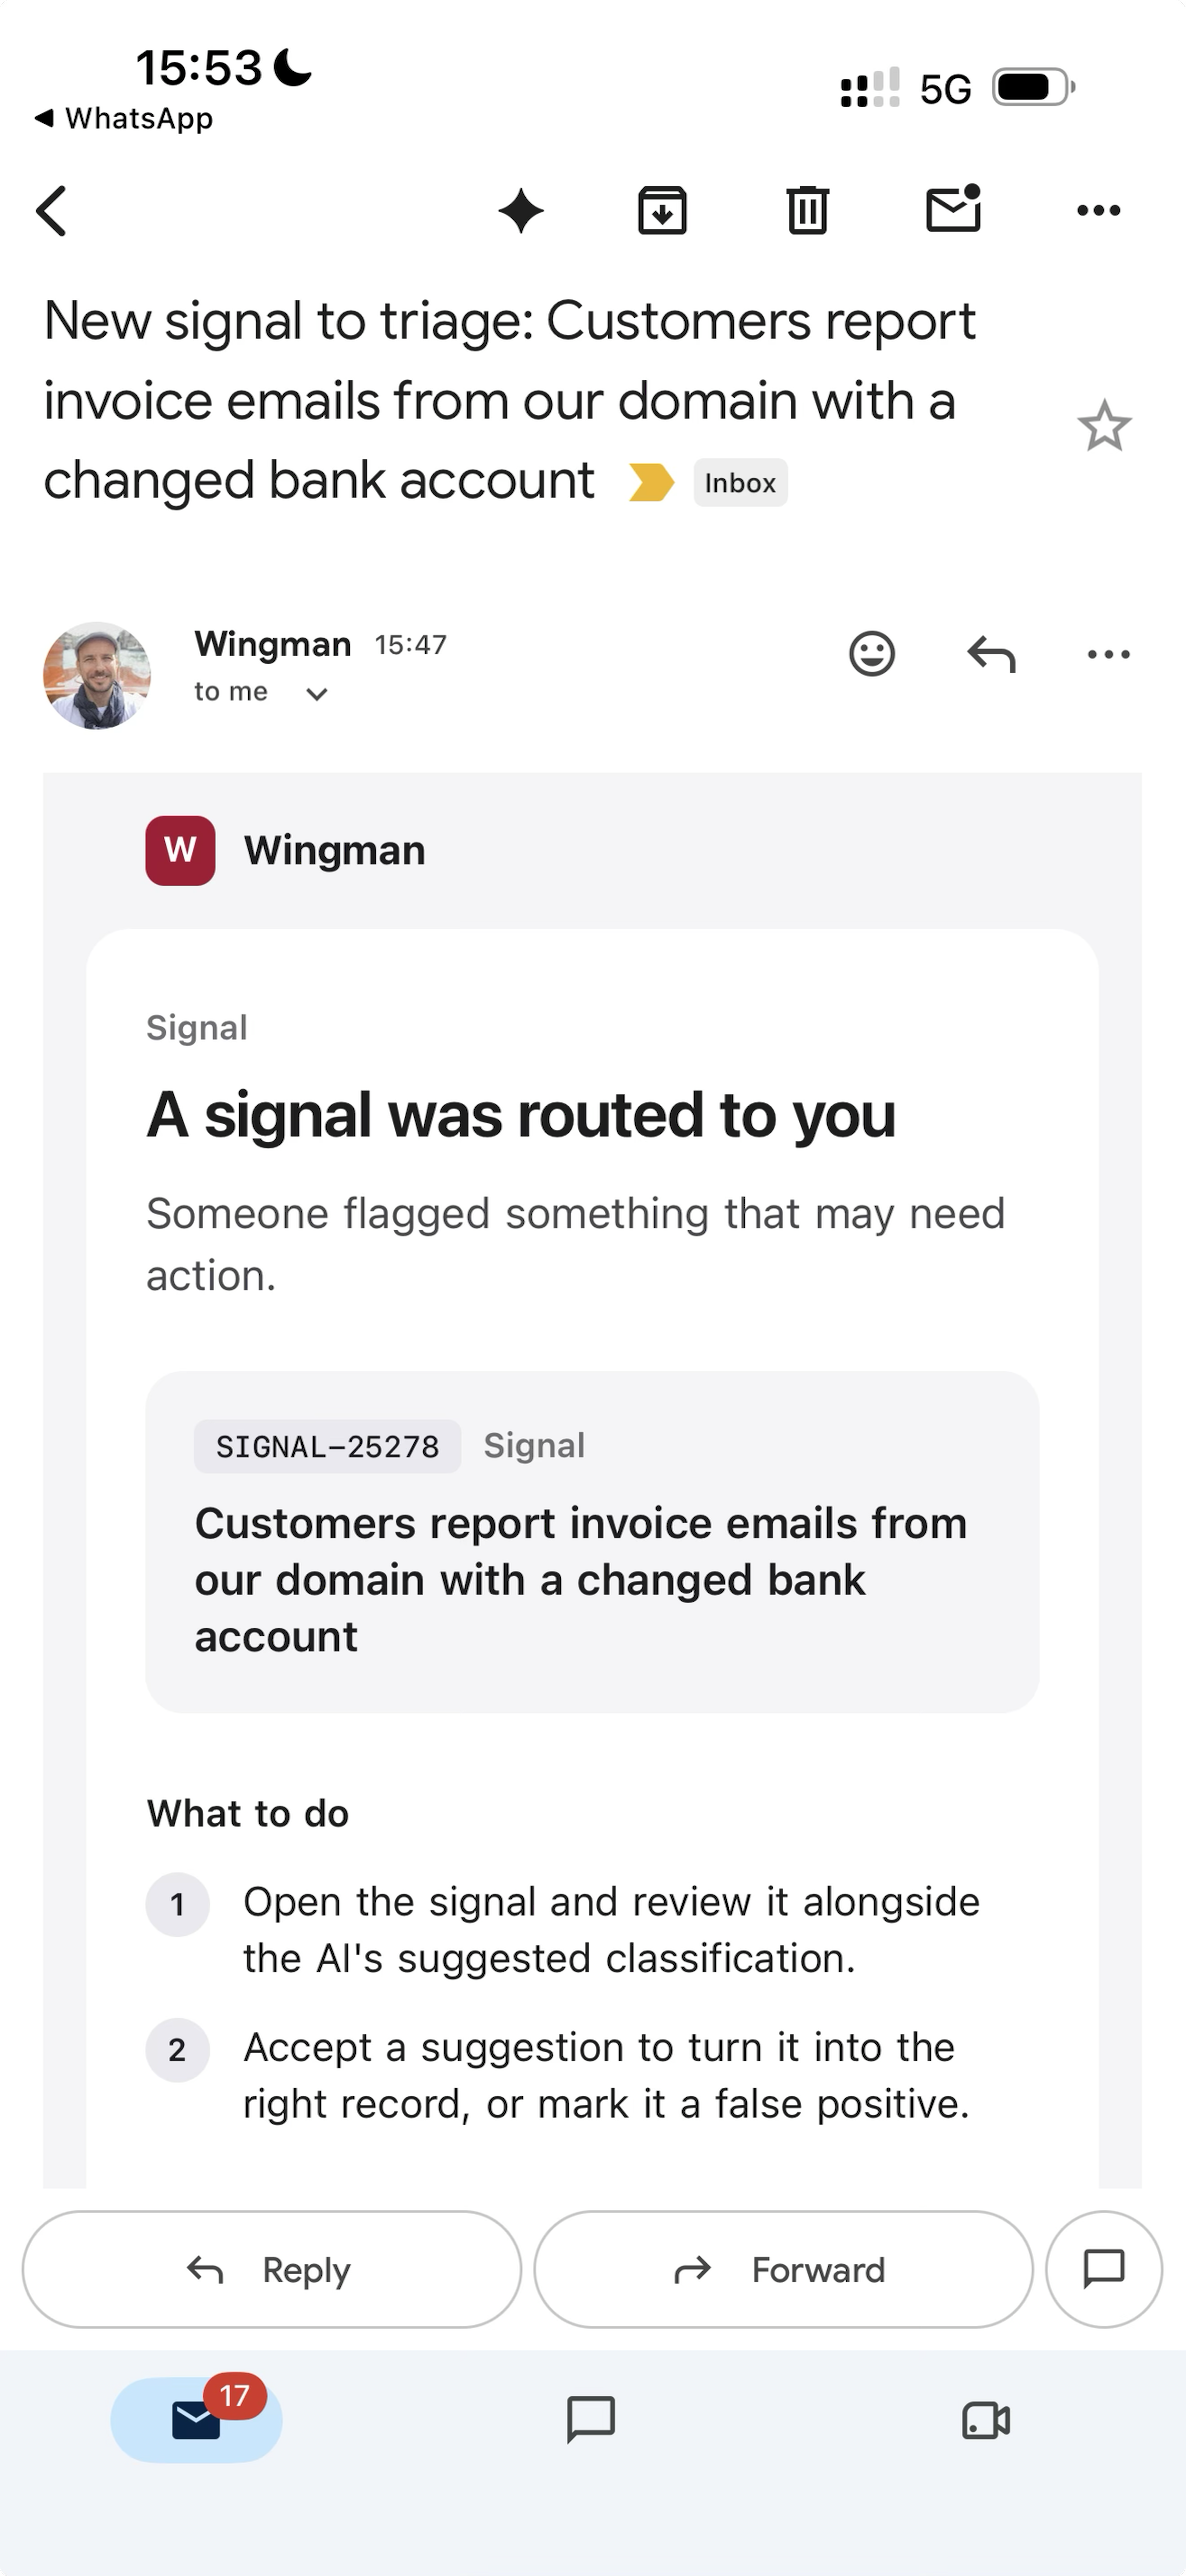
Screens for this stage · Stage 4: Escalation
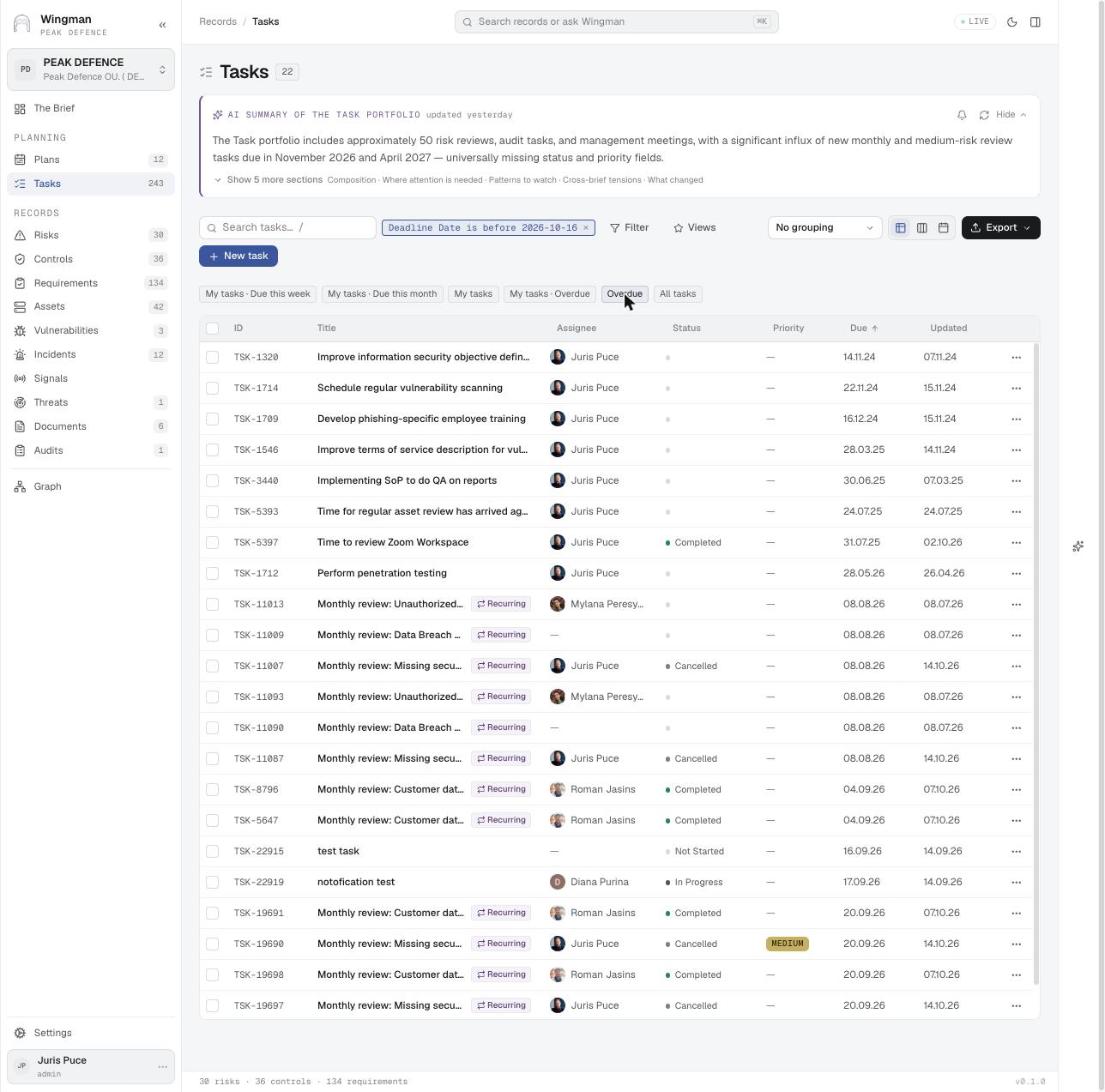
Screens for this stage · Stage 5: Signals into work
Sector angles
What this use case looks like under specific regulations.
Other use cases
Incident handling
Support every stage of an incident, from the first signal to the risk review it should trigger.
Supplier evaluation
Evaluate a supplier for feasibility before onboarding, and keep watching it afterwards.
Change management
Assess a planned change for impact, decide the controls needed before and after it, and keep one set of records as the result.
Regular reviews
Run the reviews good practice expects (assets, documents, risks, incidents, access) on a calendar instead of from memory.