Risk review and treatment
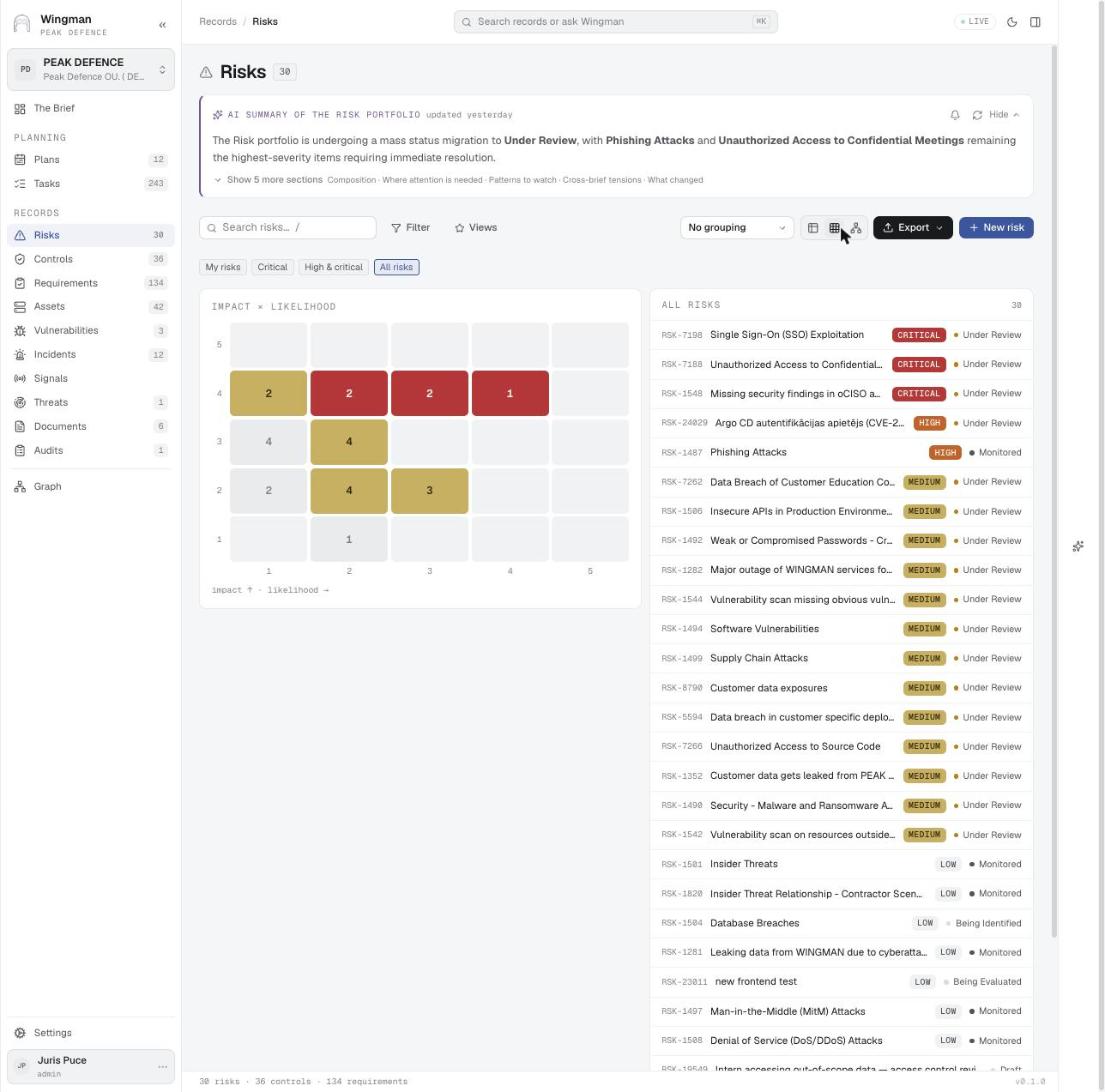
Review risks with all the context gathered since last time, plan their treatment, and keep several levels of risk consistent.
Typical requirementsISO 27001 6.1, 8.2NIS2 Art. 21DORA Art. 6
Screens for this stage · Stage 1: Scheduled review
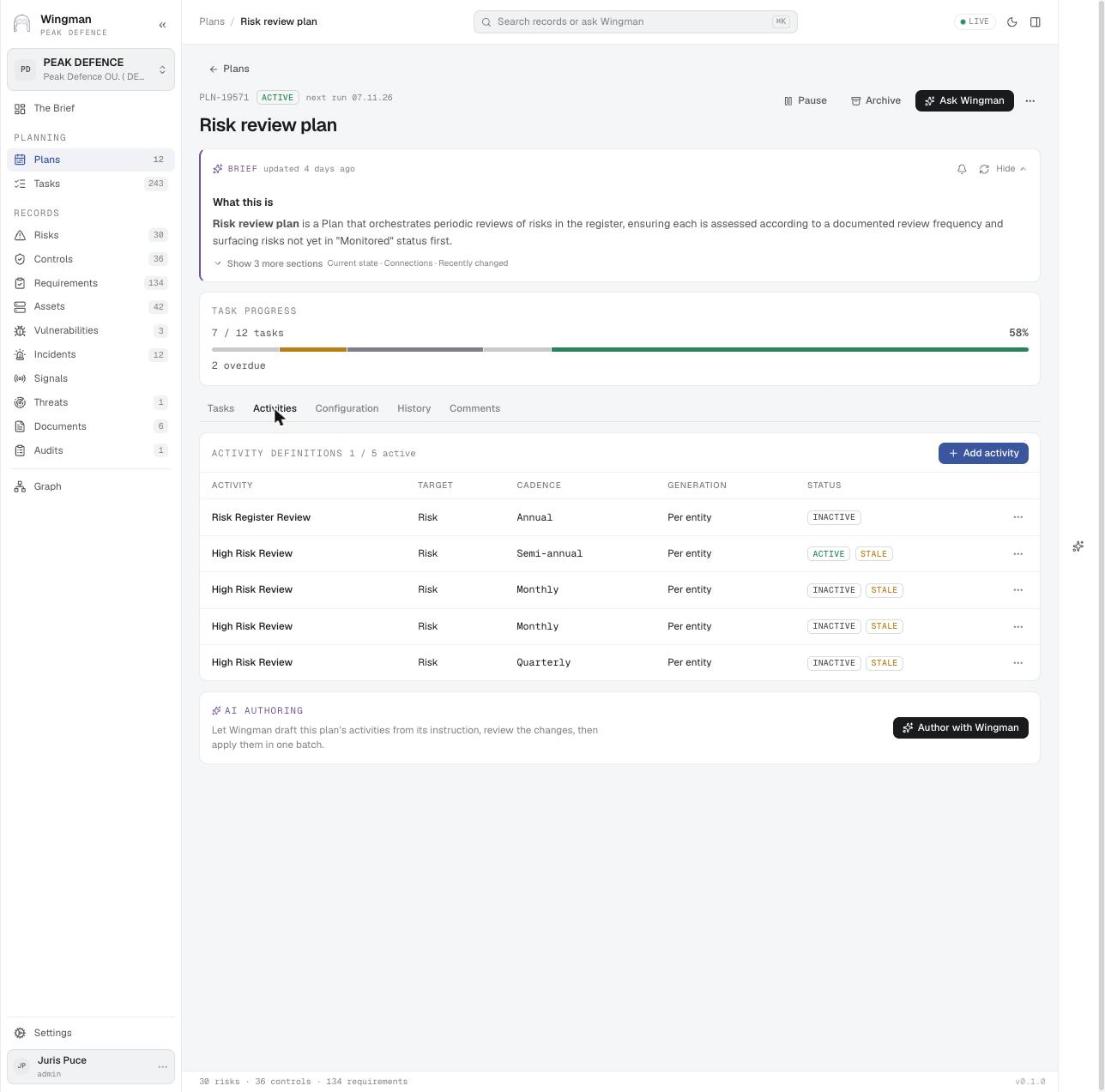
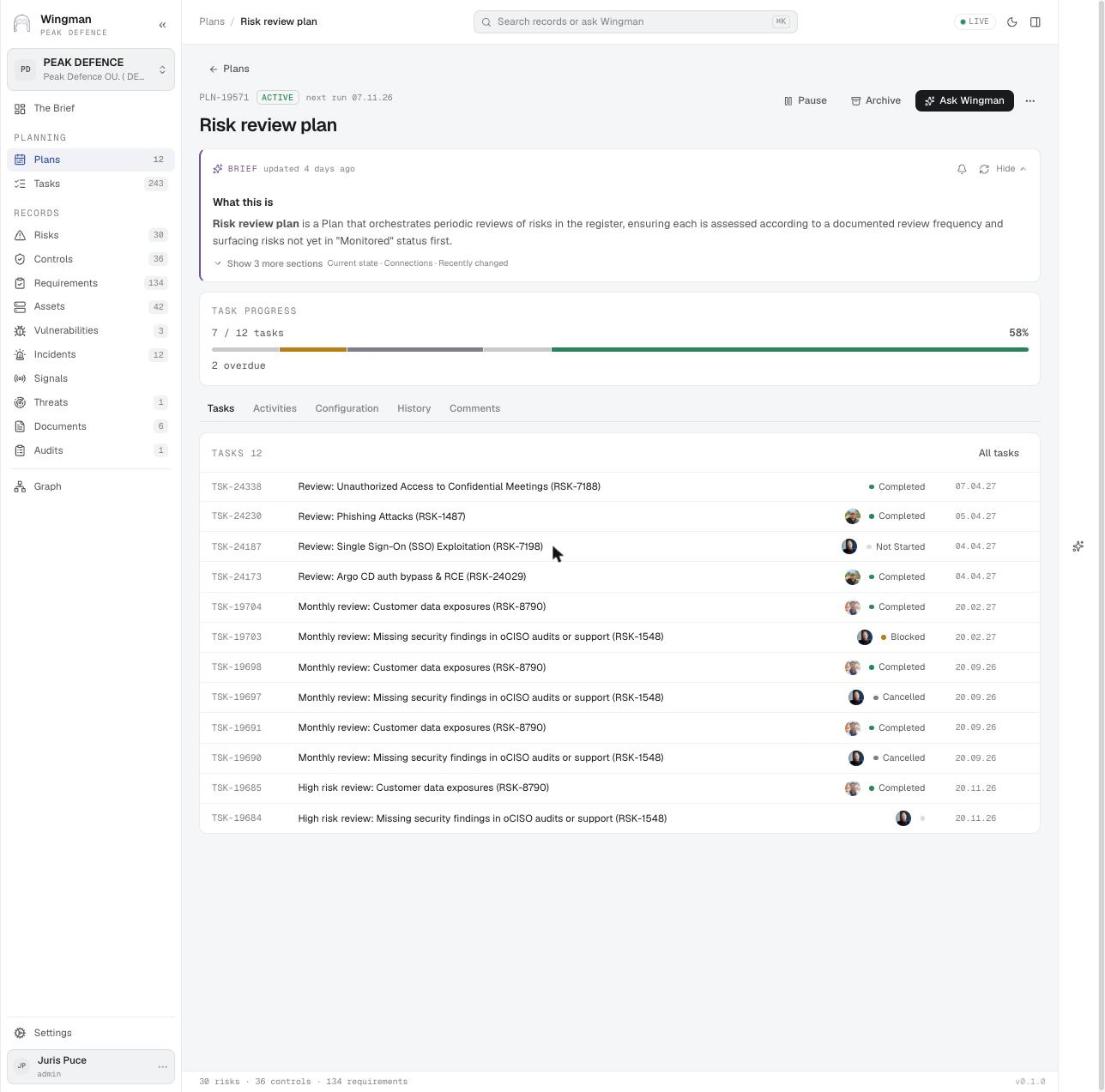
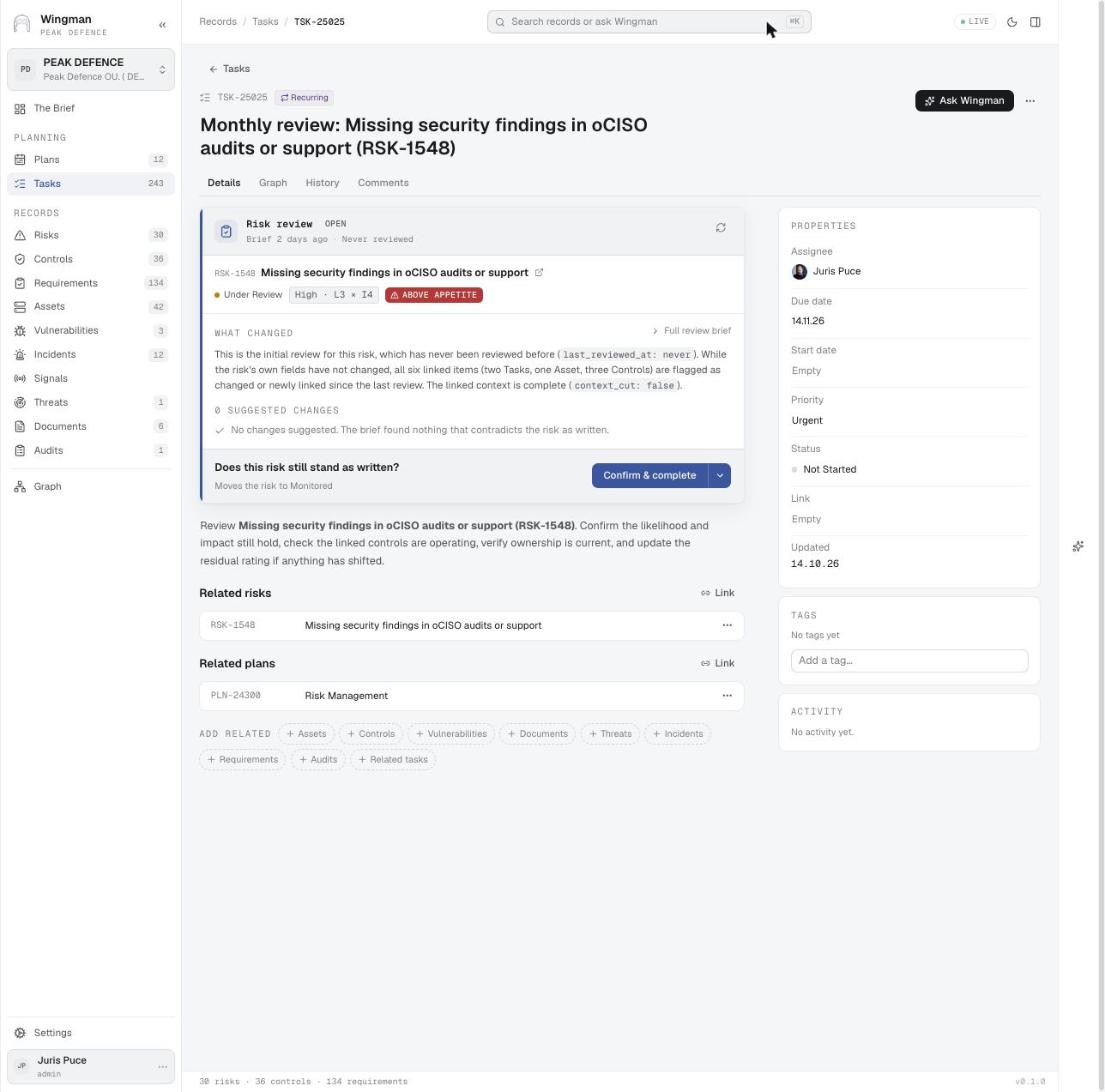
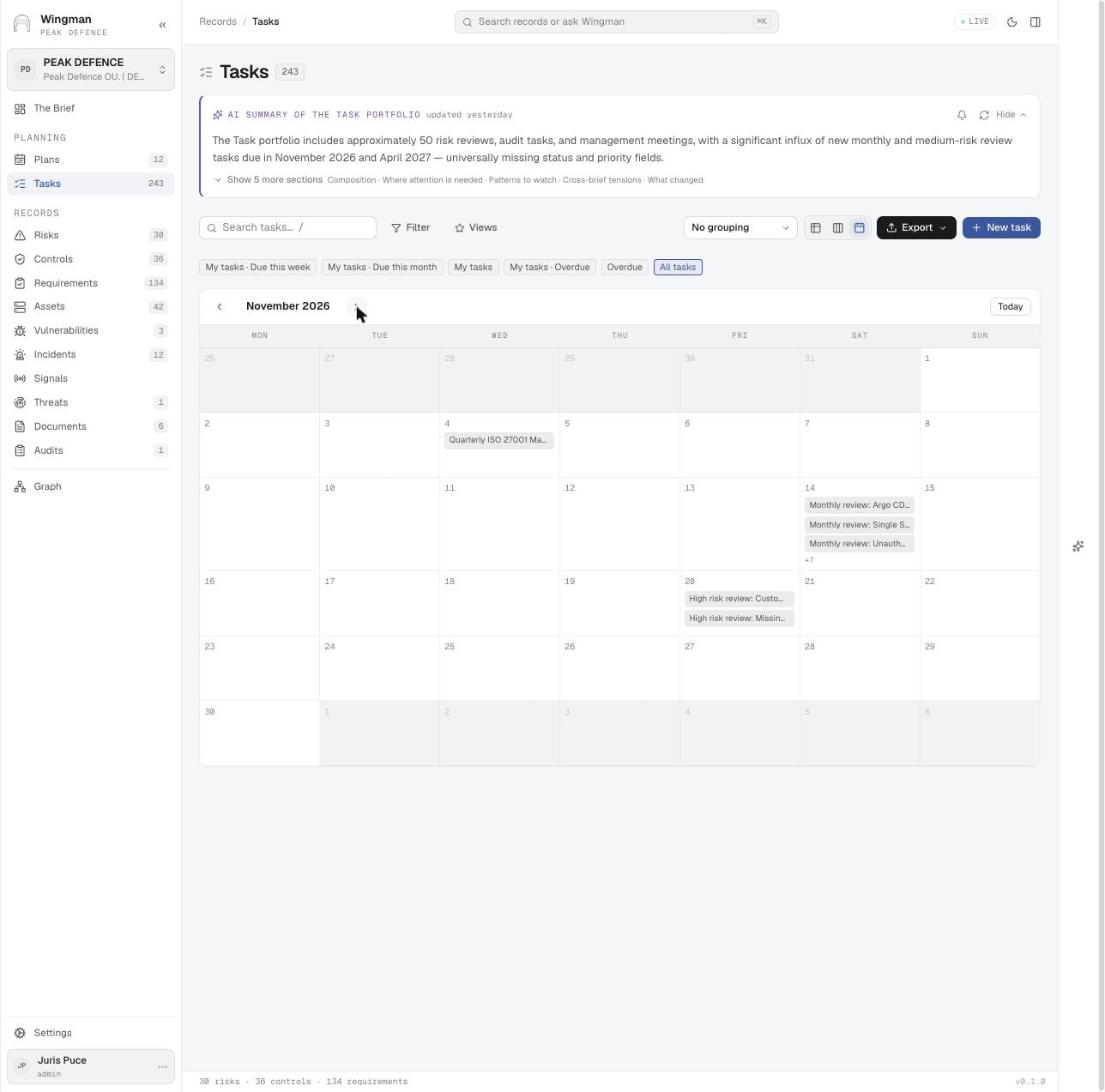
Screens for this stage · Stage 2: Context since last time
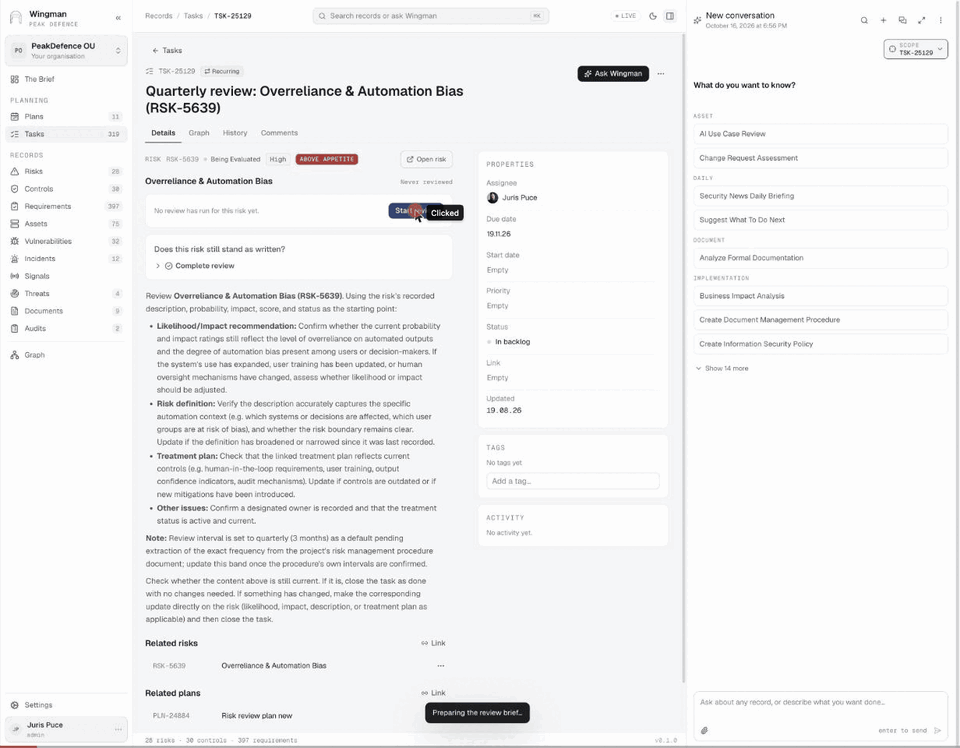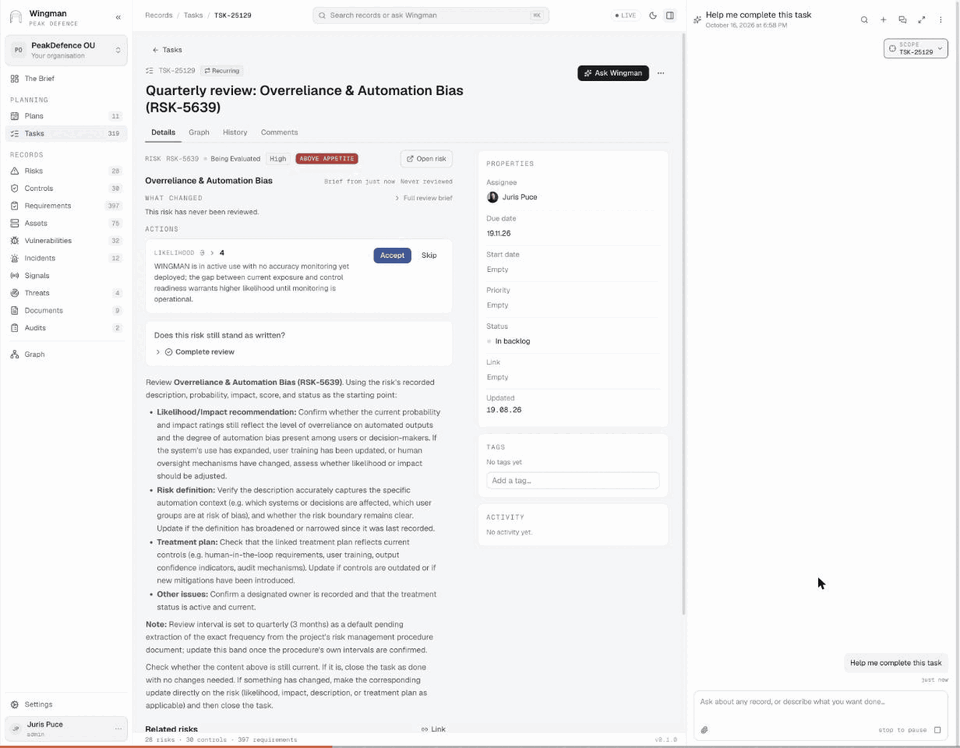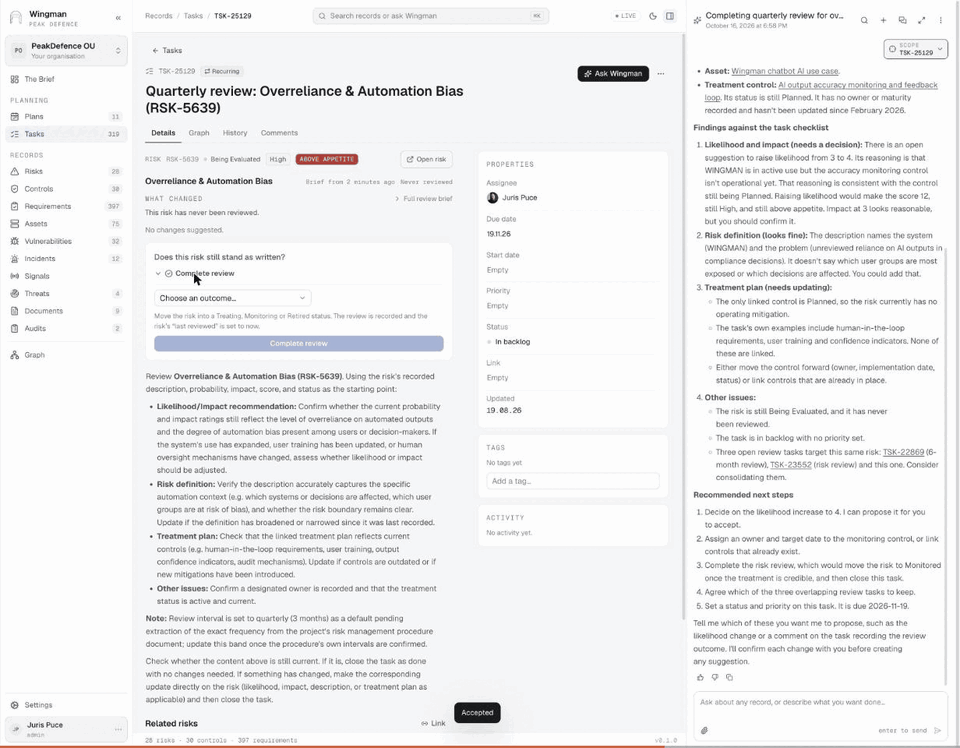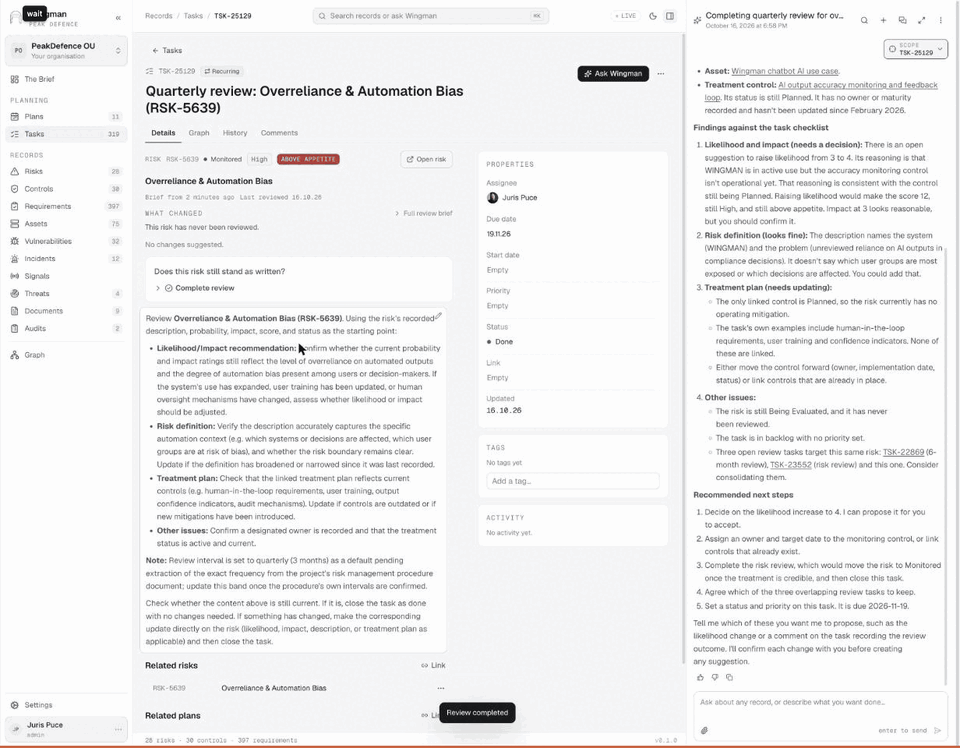 GIF
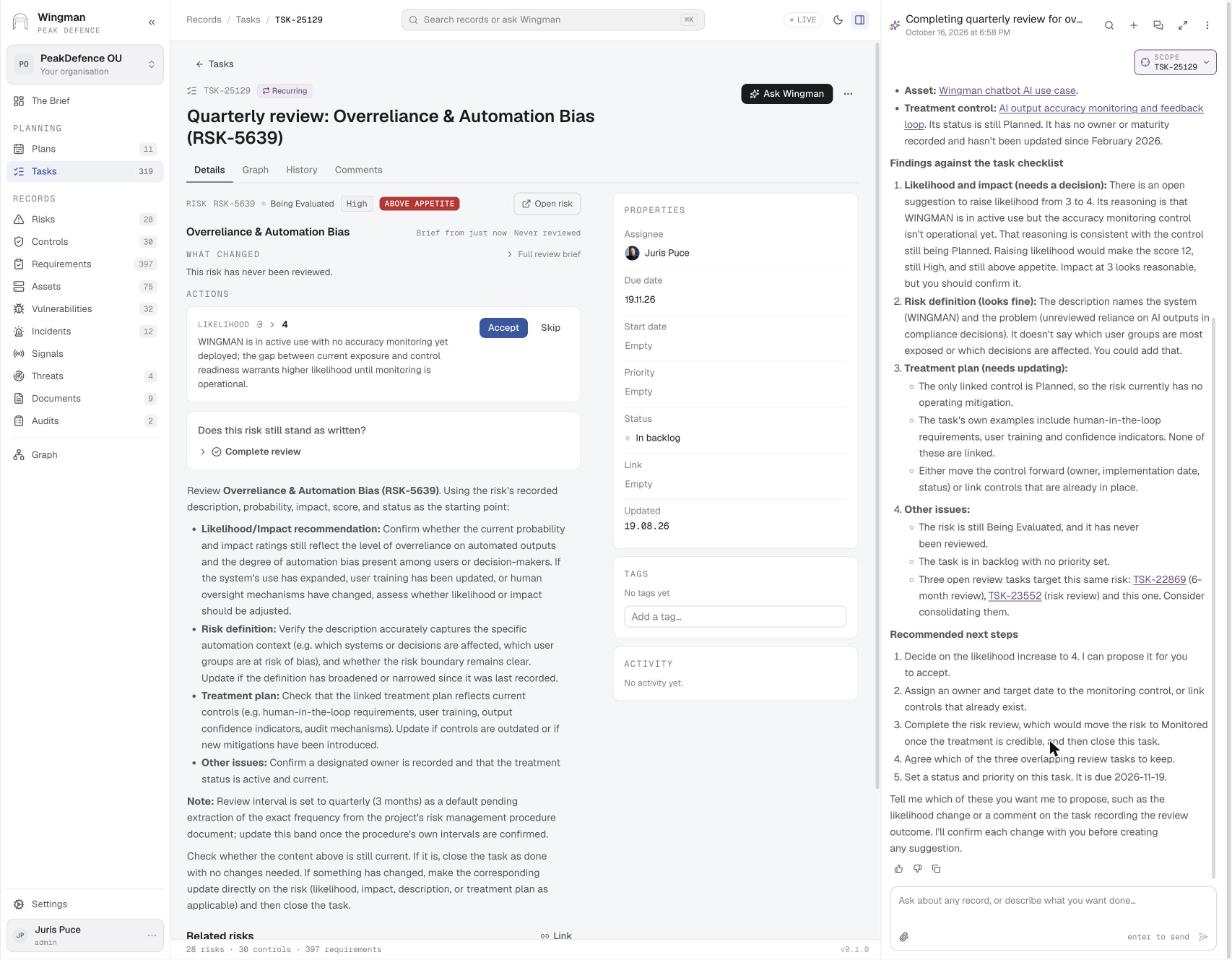
Screens for this stage · Stage 3: Several levels
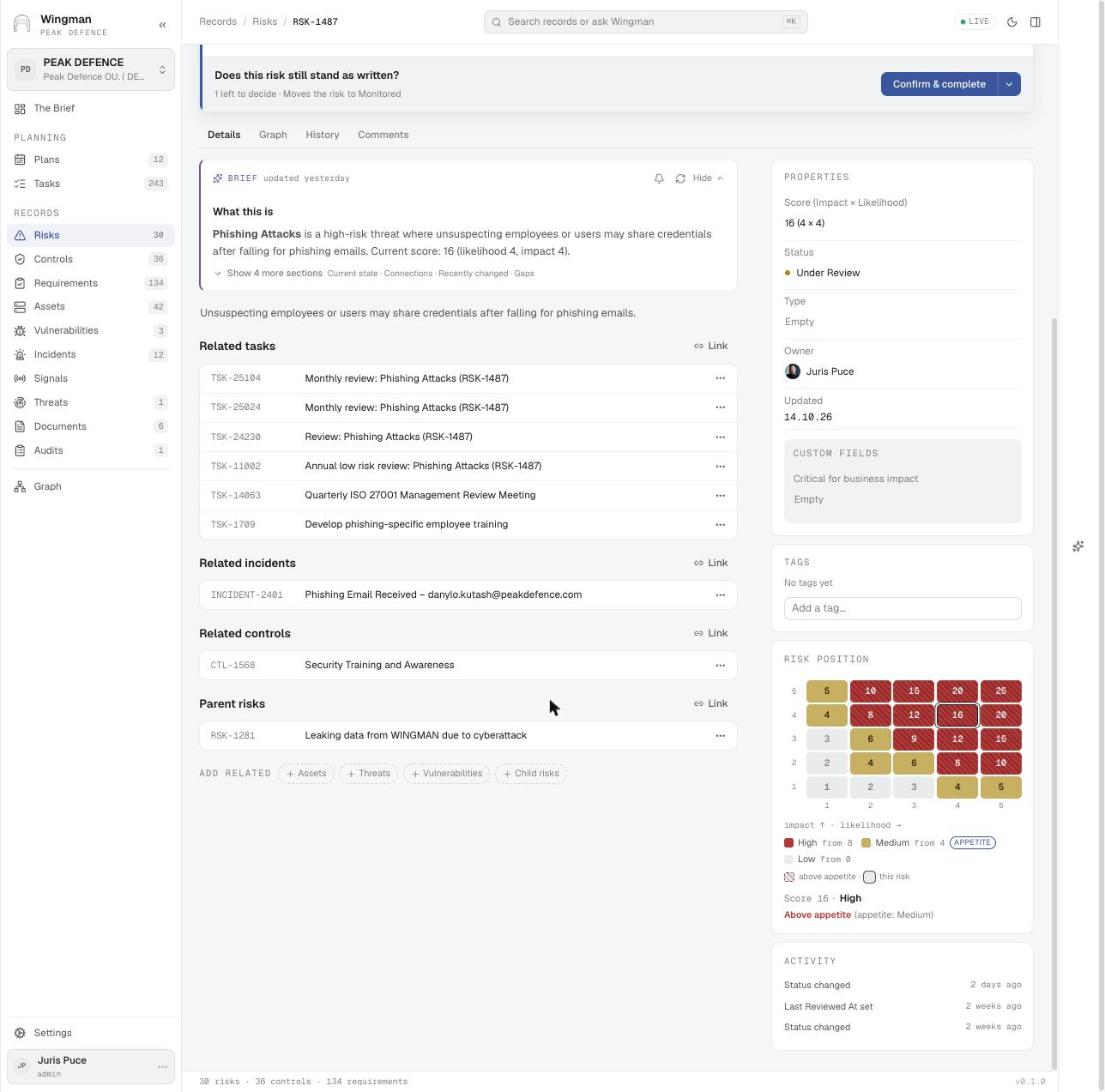
Screens for this stage · Stage 4: Treatment plan
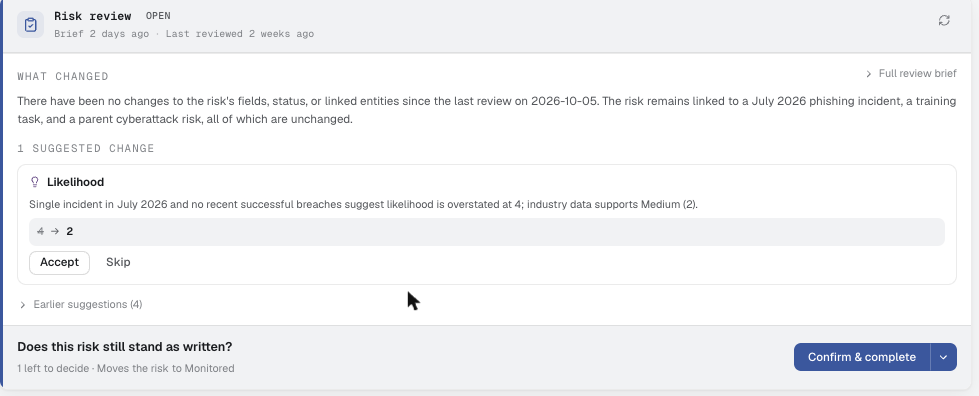
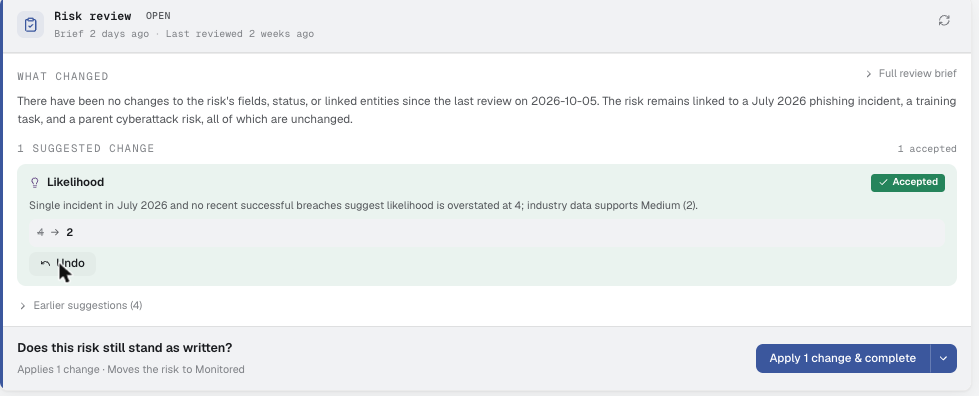
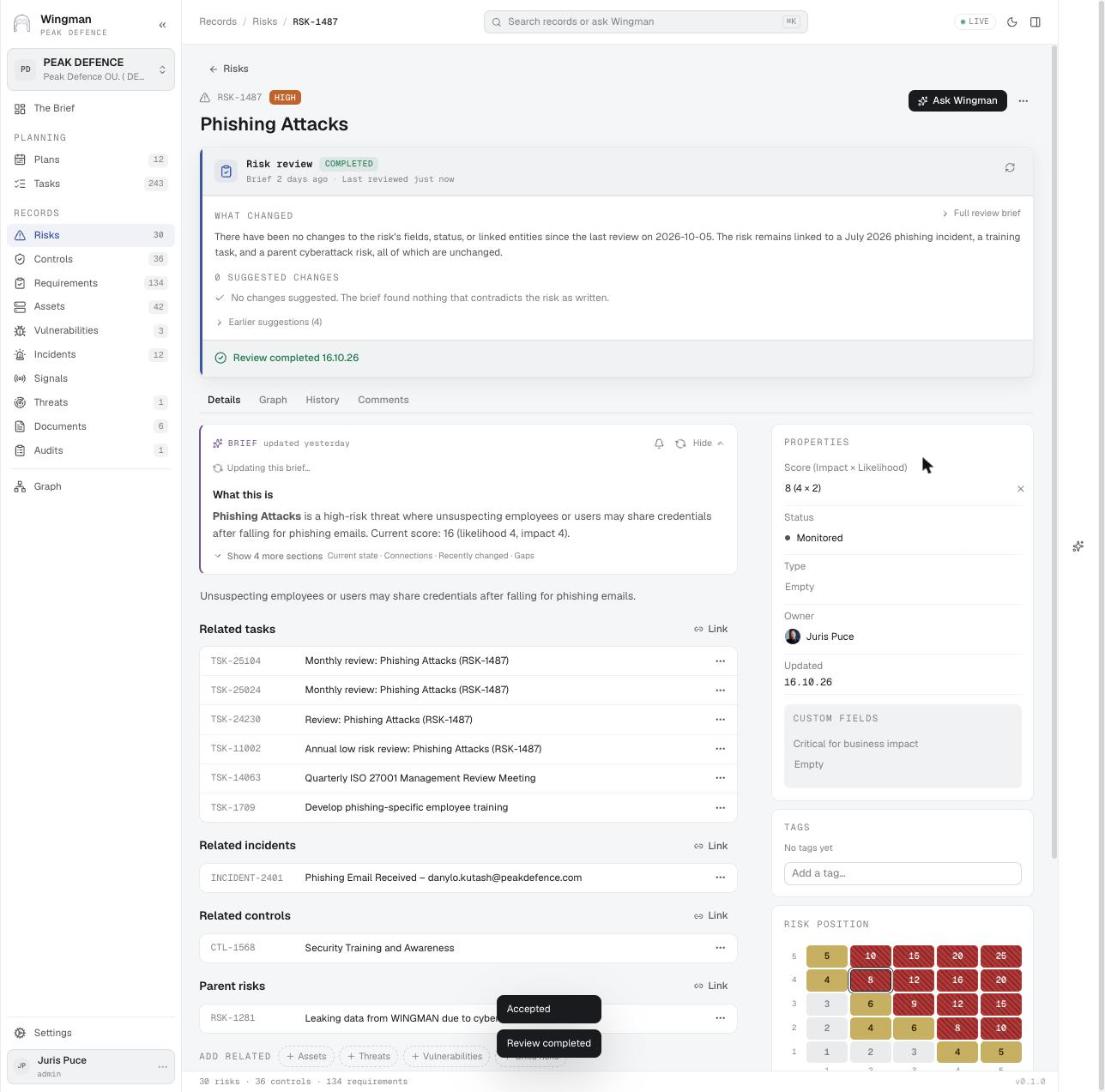
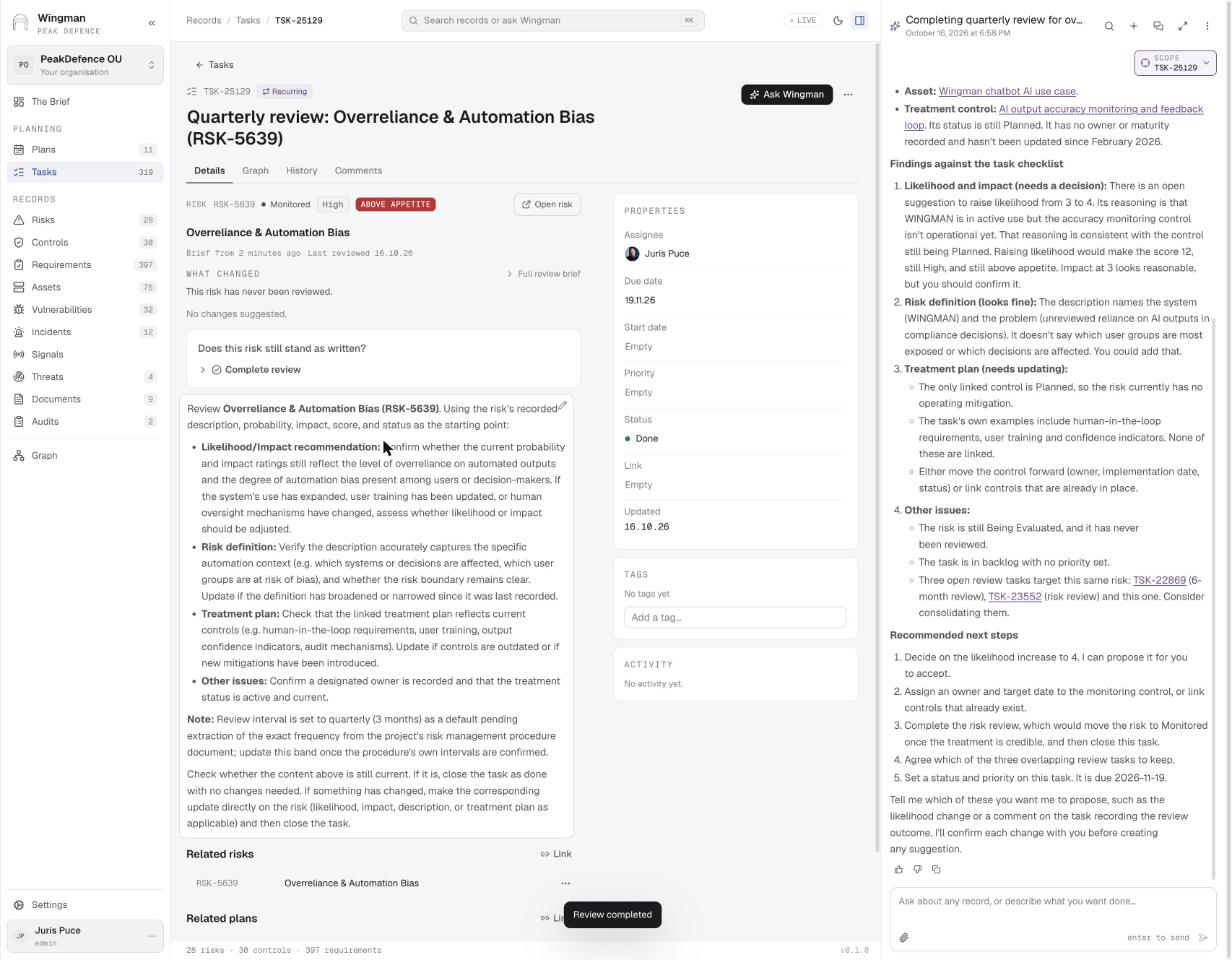
Screens for this stage · Stage 5: Register check
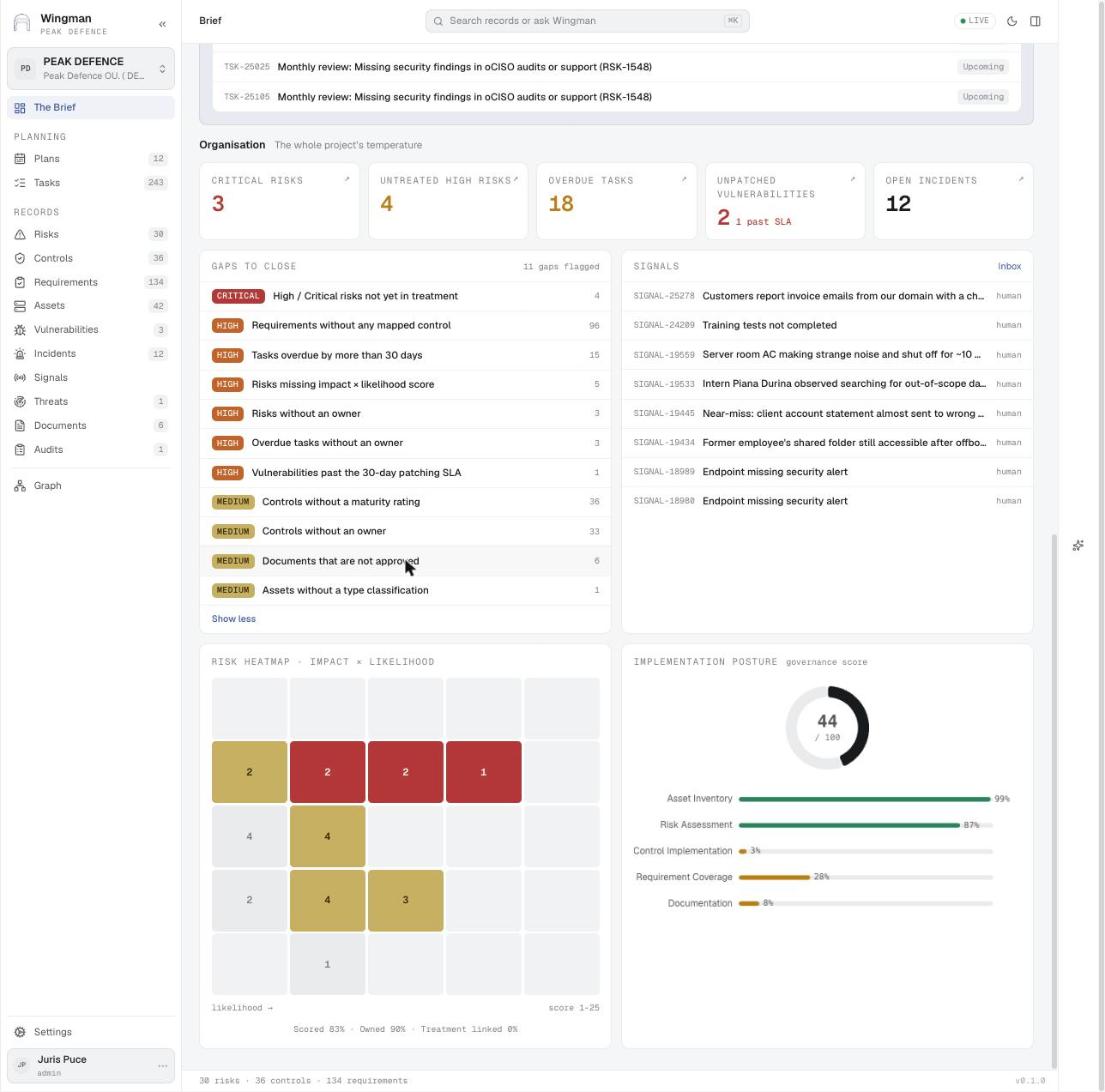
Sector angles
What this use case looks like under specific regulations.
NIS2
An all-hazards risk assessment per service, with treatments the management body can approve.
Financial sector
Risk and control self-assessment with second-line challenge, scheduled and tracked as a plan.
ISO 27001 / SOC 2
Risk assessment and treatment on a set cycle. A treatment decision changes the live Statement of Applicability straight away.
Videos


Plays from youtube-nocookie.com. YouTube sets no cookies until you press play.
Other use cases
Vulnerability impact
Assess each vulnerability by the risk it raises, and fix first what matters most.
Risk identification
Find new risks without duplicates, link them to everything relevant, and let signals start identification or a re-review.
Business impact analysis
Assess how long each service can be down and what recovery it needs, from the services, risks and controls already recorded.